Replies (115)

That's true-- I've known Peter since 1995, which was the last year that I was wealthier than Peter. We met at the famous Rene Girard seminar at Stanford University. I helped Peter launch and grow Clarium Capital from $50 million in 2003 to $2 billion in 2006 when I left. This isn't a secret and is widely known. For full disclosure, I was also an early investor in Palantir in 2005 and sold the remainder of my shares after the IPO unlock in 2021 and put the money into Bitcoin. None of this is a secret. I have a successful TradFi background, which made my trading courses and my current perspectives a unique offering. Today I condemn Palantir absolutely and wish that I had never invested. It's the most evil and dangerous corporation in the world, but it was a different world back in 2005 and I was a normie back then, who was dumb enough to believe that the company was set up to help prevent another 9/11. I knew that the CIA's investment arm had invested in it, but for some reason didn't think that was a big deal. For full disclosure, I haven't been on Peter's payroll since 2006, and I haven't communicated with him in over 2 years. You may have missed the fact that I've attacked numerous Peter Thiel shitcoin projects since 2019, most recently including Citrea. Peter is probably the smartest person that I've ever met, but has taken a very non-libertarian turn over the past few decades that I do not support. If I'm such a bad actor, why were you publishing my articles on TFTC?

Understanding Bitcoin Seed Security
A Bitcoin seed, sometimes referred to as a recovery seed, seed phrase, or mnemonic phrase, typically comprises 12 or 24 words chosen in a specific ...
That's a different person, moron. Why are you so lazy that you rely on AI?
https://www.crunchbase.com/person/matthew-b-kratterThat’s how you properly respond to an accusation.
For those who are not aware yet, this is the reason behind this childish attack.
View quoted note →But he's never once responded to my criticisms or concerns:

stacktoshi 🚀 ∞/21m
Maybe they genuinely believe the spam issue is not a crisis. Ever consider that Matthew? Sub 1 sat/vB… when has an arbitrary price floor ever bee...
It's all innuendo with the "CSAM and shitcoin friendly Core cabal" or some shit like that. I won't deny that there are bad people trying to infiltrate bitcoin development, but don't think for a second that they wouldn't also be trying to infiltrate the Knots side as well, or use the same arguments to hinder adoption.
Yeah, Odell's original dunk on Kratter wasn't a dunk really. It was news to me but not in a bad way.
But then again, if Kratter is so well connected and obviously smart and functional, why can't he see bip110 for the failure it is?
For the record, if Core gets routed around with Libre Relay etc., the answer isn't to turn Core into Libre Relay. That was the wrong signal but you can't fight spam with consensus neither. No spam project will get disrupted by Luke and Mechanic. Only Bitcoin will get disrupted by the bip110 fud and hopefully not by the fork when it happens.
I do not see the situation as an acute emergency, even if it is sometimes framed that way by the Knots side. And i agree, it would be naive to assume that any side is immune to compromised actors. Based on what I have observed over the past months, I still lean toward the Knots position.
The increase of the OP_RETURN limit was controversial from the outset. For months, the Knots side made it clear that their objective was to reverse the change. Despite that, there has been no visible willingness to seriously reconsider it. More nodes are now running Knots than Core v30. That cannot reasonably be described as a clear and uncontested mandate. Yet even in light of these signals, there has been no meaningful reflection or attempt at compromise. The obvious question remains: why?
The main argument in favor of the change is mining centralization. Without the adjustment, fee markets could develop outside node policy, allowing larger OP_RETURN data to be compensated directly to miners. The concern is that this would create long-term centralization pressure.
If the real issue is the potential for bypassing node policy, an equally effective approach would be to tighten consensus rules rather than relax OP_RETURN limits. A stricter consensus limit would make large OP_RETURN data fundamentally impossible, eliminate the bypass vector entirely, and at the same time address the broader data concern.
This is precisely the direction the proposed fork takes. It may be stricter than necessary, but it attempts to solve the same underlying problem Core claims to address, without introducing new incentive shifts or expanding Bitcoin’s attack surface.
I believe the legal dimension is relevant too, even if, in theory, node operators are not doing anything illegal themselves. The fact that they are not responsible for the content does not eliminate the practical risk. If illegal material is embedded in the blockchain, running a node could still expose someone to legal scrutiny or prosecution on the grounds that they are distributing, or storing that data.
This risk may be especially significant in developing, or more authoritarian countries, where legal systems are less predictable and due process is weaker. The recent events surrounding Samurai Wallet show that even when individuals are acting within the law, authorities may still pursue aggressive enforcement actions.
That reality should be taken seriously when changing fundemental things in bitcoin.
“For the record, if Core gets routed around with Libre Relay, etc., the answer isn’t to turn Core into Libre Relay.”
Very true, but it could be addressed by reducing OP_RETURN at the consensus level.
I believe the legal dimension is more relevant, even if, in theory, node operators are not doing anything illegal themselves. The fact that they are not responsible for the content does not eliminate the practical risk. If illegal material is embedded in the blockchain, running a node could still expose someone to legal scrutiny or prosecution on the grounds that they are distributing, or storing that data.
This risk may be especially significant in developing, or more authoritarian countries, where legal systems are less predictable and due process is weaker. The recent events surrounding Samurai Wallet show that even when individuals are acting within the law, authorities may still pursue aggressive enforcement actions.
That reality should be taken seriously when changing fundemental things in bitcoin.
it's branding.
not as original as "boatface" though, clever.
I dont think Kratter could have been more neutral and nice while making that video rebuttal. Odell's response of a personal attack to that is wild.
I fully agree. In that post, I laid out how I see the whole situation and why this conflict in Bitcoin exists, if you’re interested ;)
View quoted note →If Bitcoin can get outlawed, it will. We are winning because it can't as a whole. I don't subscribe to that part of your post.
I could get behind reducing OP_RETURN at the consensus level although to a much higher value than 0 or 83B. Make it 500 or 1kB or at least 150B. Something that's not getting in the way of meaningfully longer hashes that we might need in a quantum future but still too small for nasty pictures. But to support the bip110 madness is a bridge too far.
Maybe I’m wrong about the legal aspect. Right now, the risk seems limited. But we don’t know what could happen in the future if OP_RETURN remains open.
At the moment, block template creation is largely centralized at mining pools. I assume they currently prevent clearly problematic content from entering the blockchain, or maybe not needed?
If the long-term goal is to decentralize block creation, then moving in the direction of v30 feels questionable. Block creation without any kind of data filtering mechanism could significantly affect Bitcoin’s public perception in the future, but that’s simply my critical assessment of possible outcomes.
I would be fine with the change too. If there were at least some indication that Core is willing to change something.
So what is the plan going forward?
"But then again, if Kratter is so well connected and obviously smart and functional, why can't he see bip110 for the failure it is?"
Things that make you go hmmmmm
I'm not getting paid by anyone or any company, except YouTube which is a pittance. Here's my secret rhetorical tool that I've been using (don't tell anyone else)-- I just try to tell the truth and call out bad actors. When you don't have investors to please like VCs do, it's easy to tell the truth. Odell's hands didn't used to be tied, and that's why I admired him. That being said, he's funded some great companies like Start9 and Zaprite that I use every day, so I'm grateful for that as well. When President AOC and Elizabeth Warren come after us, we're all going to be on the same team again
have some dignity dude. You really lost yourself. Gfy
you are an idiot tho
since bip110 has nowhere near consensus it will result in a chain split when they activate
the main chain will have blocks mined significantly faster than the bip110 chain
if miners switch to bip110 days, weeks, months after activation it will reverse every bitcoin transaction that happened on the main chain during that period
considering luke calls everyone that doesnt support his fork a pedo, the tactic he will use to try to get miners to switch seems obvious
What is your opinion of David Bailey?
Those scenarios are the reason why I still hold gold
I see your concern regarding miners switching after activation. But what is your concern about bip 110?

 HODL
When investing in a bitcoin treasury CEO make sure to pay close attention to body language:
Here we have ChatGPT estimate David Bailey’s potential based solely on body language alone.
- Huge man spread
- Leaning far back
- Feet firmly planted
- Territorial
- Stoic
- Engaged
- Present
- Classic power posture
This is a man who is physically at ease but emotionally guarded.
His posture says, “You can ask me questions, but I don’t owe you energy.”
There’s a quiet dominance to the sprawl. He isn’t here to win you over. He’s here because he’s earned his seat.
Estimated Return Range based on body language:
Base Case (50th percentile):
8x –15x
Bull Case (90th percentile):
100x+
If his thesis is right and he executes (or attracts the team who can), the detachment and quiet confidence signal the kind of world-builder who changes the rules instead of playing the game. Bitcoin-style asymmetric upside.
If I had to assign a single expected return number based on a power-weighted average of outcomes:
~28x expected return
That’s factoring in:
• 10% chance of 100x+
• 40% chance of 10–20x
• 30% chance of 2–5x
• 20% chance of total failure
High volatility, high asymmetry. Definitely not a “safe” play, but could carry a whole fund if right.
In summary: Do not fade a man spreading his legs this wide.

Not sure I'm getting the reference. American Hodl is married with kids, afaik. And generally like him, but he did sorta promote these investments 😞
lol I dunno. Didn't even think about that until you pointed it out
That doesn’t explain what bip110 actually does and how it’s a threat/attack.
How/why does it reverse transaction?
You guys need to do some sort of deep dive video explaining your side with some actual facts.
Just listen to the most recent RHR
Core started this! with their reckless OP_RETURN policy. This is on core.
While true, irrelevant. The risk of a chain split is not zero. The risk of csam on the chain is also not zero. The question is which is the bigger risk. I can see arguments for both.
Stonks are shipcoins.
Him responding to this attempted character assassination is
1. Appreciated
2. Prompt
3. Clear
This is likely deliberate as this is in stark contrast to those he has been publicly criticizing as of recent.
But it will only reverse "invalid" (relative to BIP-110 consensus rules) tx, most likely spam, not normal tx, correct ?
Because it’s more likely that bip110 will succeed than not. And even if it fails, it’s the right approach for the problem trying to solve and some battles are worth fighting for even if the odds might look against you.
They always skip the important parts.
Glad to have him on bitcoin's side now.
How childish does this have to get before it gets productive again?
No way. Is this true? Did clawbot verify

Matt Odell's position contains an inconsistency:
1. He opposes BIP-110 — a soft fork that would limit arbitrary data at consensus level
2. He doesn't oppose Core v30 — which enables the very data growth BIP-110 seeks to limit
3. He's against Knots — the client maintaining stricter defaults
This reveals something important: his opposition isn't about the outcome (data bloat), it's about the mechanism. He appears more comfortable with:
· Gradual, default-driven change (Core v30's policy shift)
· Than explicit, consensus-level limitation (BIP-110's soft fork)
Data bloat through accumulated OP_RETURN transactions achieves similar centralization pressure over time.
The network is already demonstrating what decentralization looks like:
· Core's share dropped from 88% to 78%
· Knots grew to over 21%
· Users are voting with their machines
This is decentralization in action. Different clients, different philosophies, all operating on the same chain. Matt's apparent preference for a single client contradicts this organic diversification.
Is decentralization having multiple clients with different policies?
· Or is it maintaining a single dominant client with permissive defaults?
Matt's position suggests the latter—which, doesn't fully embrace what decentralization actually means.
View quoted note →No, that is not what will happen. All mined blocks become invalid. So all transactions in them become unmined. Unless they happen to be mined in the other chain too.
Perfect time for a a large double spend...
Even considering an approach that might cause a reorg is hostile to bitcoin and bitcoiners.
Dude sell courses on how to buy bitcoin lol
But won't BIP-110 valid tx always be included in both chain ?
You're right to question why someone who claims to champion decentralization would:
1. Oppose BIP-110 (limiting arbitrary data) while accepting Core v30's OP_RETURN expansion that gradually achieves the same centralizing effect
2. Dismiss Knots (21% of nodes now) while insisting on Core as the only legitimate client
3. Defend figures with documented Epstein connections while attacking those who demand accountability
It was power to the plebs. Now it’s power to the VCs.
It’s so crazy cause I was all for knots months ago. But you guys have completely lost the plot with these ridiculous bips. If you want to change consensus and not node policy literally go fork yourself.
You mean if the majority of the network literally goes back tens of thousands of blocks and has enough hash power to not only get back to the same place but surpass current hash power? What faith you must have in BIP 110 being THAT compelling!
That's not how that works. Nothing gets "unmined" The scenario ODELL is trying to describe is if no one supports BIP110 that chain stops because of so many invalid transactions on the main chain then miners switch completely to BIP110 and mine literally tens of thousands of blocks faster than everyone else can mine a single block on the main chain.
I hope I don't have to describe how improbable that outcome is.
The difficulty adjustment is total network difficulty. That means the work would have to be the overwhelming majority hashpower continuously. Without ANY of that work appearing to the main chain as the highest block. Then after 10000 blocks the spam compliant miners would have had to not continued to mine AT ALL or it wouldn't just be N+10000, it would be N+10000+all the blocks mined after hash power switch.
Suffice it to say this is vanishingly unlikely and really supports the "a government could just mine more blocks" FUD.
It’s a threat to the donor/funding mechanism of Core/Odells companies.
Only if the miners on both sides mine at the same speed and there are no RBF transactions. And miners chose the same txes.
We are all on a journey... I used to love google and their products, I used to think Elon was doing good for humanity (many still do), I used to believe in many things as a result of "giving the benefit of the doubt" reinforced by the programming we were born into... In the end, those that can rise above their incentives to do what's right, regardless of the consequences and contrary to what they used to believe or what is popular, gain my respect and admiration. Those that double down on false beliefs to protect their standing in the fiat slave system, and demonize those that don't, are very easy to read over time as they exhibit the same actions, reactions, and demeanor.
With that said, I have immense respect and admiration for
@Matthew Kratter @Luke Dashjr @npub1wnlu...n3wr
Bitcoin is an impenetrable barrier to stealing human energy over time... Energy which was used to create the immense control structure that we wish to escape. To bring freedom, Bitcoin must remain absolutely sound as money, everything else is a distraction and a gradual attack and erosion of that.
This must be nonnegotiable, no matter the chaos, and will always (initially) come from the intolerant minority. Onward.
It is relevant. Core created this problem. If they reverse their OP_RETURN policy, things will cool down. It's up to them.
OK, I see the double spend reorg risk now, that would indeed be bad, but if BIP-110 would initially get accepted by most miners (55% signaling I believe) would you consider that as the ideal scenario ? (Since BIP-110 limits adjustment seams better for the protocol overall)
But at least he is unbelievably smart in some areas, unlike Gloria or little Napoleon Poinsot who are just hybris 🤪 Insanity and genius are close neighbours
I was under the impression that that is what Luke has said he wants to do? That they only need a few percent of miners to get this going. I will be honest here, I probably do not pay enough attention to all the details here.
Some of my objections to BIP110 is the "rush", and the proponents trying to incite panic and fear. And it also being "temporary", which to me sounds like the opposite of sound money.
Again, with a 60/40 split in either direction, 1-2 block could be orphaned but that is not new. I can see if one does not like the restrictive nature of the soft fork, it seems like an attack but it is literally just how consensus works.
The only way I see an increased orphan block risk over 1-2 blocks would be if so called spammers incentivized the miners repetitively with multiple high priced non-compliant blocks. But then it would be a spam attack, not really the fork's attack.
I don't think a flagday activation is smart. If a majority of nodes and hashpower like these restrictive consensus policies, thats just how consensus works.
Fear is being utilized everywhere.
"Aren't you afraid that the Knotzis are going to chainsplit?"
"Aren't you afraid of CSAM on the blockchain?"
"Aren't you afraid that BIP 110 opens the door for governments to control bitcoin by pushing a softfork?"
"Aren't you afraid that your node will have to be a super computer to even validate transactions?"
Everyone is being a fear monger. Sift through the noise and find the truth.
appreciate you, Odell 🙏
I wish we could all see some good faith adjustments from Core. I don't know enough to even know what that might look like, but it would go a long way to calm things down. From the perspective of many of us, v30 was handled so badly that it's hard not to attribute bad motives to it.
Only one side is trying to rush through a consensus change.
And, please enlighten me to what that "consensus change" is.
Bip 110 would have the effect of putting spam into the UTXO set, harming node decentralisation, and the strict relay policy of Knots would centralise mining by encouraging miners to use out-of-band systems. It's an attack on all the important aspects of decentralisation, including Luke's desperate attempt to make himself the lead developer
This debate ended in early 2024 when, in response to Mara's Slipstream, the bitcoin network (without asking permission from Core or Knots) relaxed relay policy in order to defend mining decentralisation
How long did it take before it became obvious who won the blocksize war?
not sure where you pulled “tens of thousands of blocks” from - a week is about a thousand blocks, a month is about four thousand blocks
its how the fork is designed and their intention
they believe that if they start to get any type of momentum on hash pivoting to their chain, the rest will follow due to the risk of the reorg wiping out their rewards
they will likely use threats to try to make it happen and will probably fail but its fucked up regardless
I was thinking you meant a delay of 3 months and maybe I was being hyperbolic but the point stands regardless, anything past 6 blocks is a vanishingly small likelihood if the support is as low as you think. Chainsplit risk is zero barring the proliferation of a URSF client. There are two possibilities:
1. BIP 110 fails immediately (10 noncompliant blocks after activation makes the hash power contest almost unwinnable for BIP110)
2. BIP 110 has moderate to high support making it the main chain.
Yeah. Maybe both Knots and Core will think long and hard before they make changes that the plebs disagree with. Ultimately it will force long term thinking. The BIP would have never been necessary without the OP Return issue.
we have never seen an attack like this before, and i wouldnt underestimate them, they will likely try to keep the bip110 chain limping along while spamming the other chain and threatening people
Hey Zaytun, your rational questions will not be answered here.
This is a place for non factual… “you shouldn’t look over there” rhetoric.
If you look over the fence… just don’t look over the fence. Blindly follow us instead. Lol
I am being facetious obviously. I don’t want it to be taken out of context though.
#runbip110
#bitcoin
The only incentive is valid block propagation. To ensure payment. The only way you can ensure valid block propagation is to make blocks the highest percentage of blocks would find as valid. BIP 110 being stricter would have an advantage via this incentive. Because:
BIP 110 valid =Core valid
Core valid ≠ BIP 110 valid
That is the asymmetric incentive.
Well, except BitVM who've been working hard on scaling Bitcoin and will be banned from building onchain cause...?
How embarrassing for you. Now you're promoting a hardfork?
you wont learn anything re BIP110 listening to the most recent RHR. @odell's rants were all emotional, personal attacks, with a FU conclusion based on speculation of the worst possible outcome of the BIP110 soft fork.
A chain split will create two chains, like when Bitcoin Cash happened and lost the split. It became a minority chain no ones care about; anyway there were funds loss because at first transactions would happen on both chains at once and stuff like that, it was a messy process & we definitely don't need that now.
You didn’t explain what was the attack vector. All you said is Luke is calling people pedos and forcing them to upgrade. And even this is not true.
Bip110 is a soft fork you retard
You lack respect, integrity, and intelligence.
Kratter, Luke, Mechanic, are all ten times the bitcoiner you are. You are a paid off VC boy.
Get humble and run BIP110.
If you have watched any video from late 2023 onward you will see that all he’s doing is criticising the guy and all other MSTR copies who other influencers shilled the entire bull market.
Own your mistake you loser.
Anyone around 2015-2017, or indeed anyone with two functioning brain cells, can see where this is heading. Perhaps you were busy in highschool back then? Or into PoS or something cool like that? If it does happen, which sadly is starting to look likely, please make sure you don't sell it for BTC. Do Bitcoin a favour and ride your fork to zero like Ver/CSW etc. Good man. Remember , "babies are dying"
Lmao you’re even more retarded that I initially concluded. Bip110 is the small blockers equivalent as far as those two are comparable, but you’re too dumb and deranged to figure this one out, so…
Thank you for helping me understand the personality types evangelizing BIP110.
That’s easy. They’re not the pedos, spammers and scammers.
You're so right. Thanks again!
Care to put your prediction for September into words so I can bookmark it?
Apparently Bip110 doesn’t break BitVM.
"The 257-byte control block limit constrains large Taptrees. Advanced smart contracts like BitVM may need to wait until [BIP110] expiry or use testnet/sidechains." source: bip110.org — though on the same page they also pretend that "All known monetary use cases remain fully functional and unaffected.", which is quite gross.
Btw, let me add that blocking consensus upgrades will also delay any covenant update, that are required for Ark to become viable, as well as to upgrade lightning... Since I assume we all know what "temporary emergency measure" means.
Pretty interesting consequences of a sloppy design... If prevent harmful content on the nodes was the point, cap-sizing OP_RETURN would have been sufficient, but ofc they had to overdo it to retaliate and show everyone who's the bitcoin boss, and now we have this mess instead... Lame. :(

>> "based on speculation of the worst possible outcome"
It's important to remember that this is the level at which changes to bitcoin should be thought through. I saw some snippets of the RHR episode and honestly yes,
@ODELL is extremely emotional in his critique. But that aside, most of his points are probably valid. Except the "miners switching after activation" argument.
I mean. Because in that case, there would be consensus to move over - despite the transactions that would be erased. I guess consensus is literally the argument to accept rolling back those txs.
However, the point that his adversarial thinking here is justified is contradictory to core30 crowd, and especially
@Jameson Lopp argumentation.
In another node, lopp "prepares" us that Knots crowd might ingest the blockchain with child pornography to prove their point.
Well.... if an attack vector has been introduced to bitcoin, and you helped introduced that attack vector.... then you're probably to blame if that attack vector is actually utilized. You don't really get to decide what the motive of your opponent is if they decide to perform the attack.
This became a longer note than intended, but just a TLDR to end it with:
- Odell is thinking in adversarial terms regarding bip110 which is important and arguing that it wont fix spam anyway
- but not about core30 which from my understanding doesnt fix spam at all
- lopp is being a bitch about introducing an attack vector to bitcoin
- maybe nobody should've merged a change, however small, to bitcoin core, if that change was this controversial
Can you link the exact source? All I found on the website is this disclaimer, that claims complications around BitVM, not that it becomes unviable. Also, it’s absolutely normal to disable upgrade hooks for other soft forks while this one gets adopted. Not to mention any soft forks will require months or years of discussion and signalling before it has any chance of going live. It’s common engineering logic - don’t start building extensions around your house while its foundations are shaky.


I gave you my source. Also, I think you misunderstood how it works: it will prevent any consensus upgrade for the time it is active... And we all know how long emergency, temporary measures can last. Though in by view, "temporary" measures on something like Bitcoin make no sense start with. Either it's good and we keep it, either it's not and it never touches consensus. 🤔
"Acceptable short-term tradeoffs" is doing a lot of heavy lifting in that FAQ. Temporarily breaking smart contracts and disabling upgrade hooks to filter data you don't like. Name one temporary restriction on a permissionless system that actually stayed temporary.

I don’t understand your framing of “emergency temporary measures.” That logic applies to centralized systems where a small group can extend powers at will. This isn’t that. It’s a soft fork with a built-in expiry at a specific block height. It self-expires. Extending it would require a new round of consensus. And if it’s not working as intended or if meaningful monetary use cases emerge over the next 18 months - I don’t see how it would get that consensus.
BitVM falls into that bucket too. At this stage it’s not a proven monetary use case. It’s closer to an Ethereum-style experimentation sandbox than to something that strengthens Bitcoin’s monetary function. There isn’t a single production-grade deployment demonstrating durable demand - just philosophical whataboutism about what might exist someday.
What puzzles me about the criticism of BIP110 is the inconsistency. If it were permanent, critics would call it reckless and irreversible. When it’s explicitly temporary precisely because it could carry risk - they still call it reckless, now because it might not be permanent. It sounds less like risk analysis and more like reflexive opposition. 🤔
Is it correct to call it an attack?
BIP110 intention is to reduce spam stored on Bitcoin network going forward.
Seems like a fix for unintended use of Bitcoin as storage for arbitrary data.
Is there a good reason to not signal for BIP110 and allow spam on the network to continue?
Fuck off bot
Maybe because different people have different opinions? Btw, this is not "my" framing, this is their framing:
"The one-year deployment allows the community to evaluate the impact while developers work on a longer-term solution. Some restrictions would severely constrain future upgrades if permanent, but are acceptable for a limited time to address the immediate crisis."
In other words, this solution sucks, but we have nothing better right now & there's an urgent matter that needs to be adressed right now. (which urgent matter, we are left to our imaginaion 😂)
Sincerely, I find it painful to discuss this matter with you since you talk like you know, and yet didn't even read the proposal itself. Also, that moving the goalpost each time proven wrong... That's not serious: Bitcoin deserves better considerations & care when it comes to touching the consensus. 🤔
I’ve read the proposal and a bunch of opinions from both sides to form an opinion. For example you quote certain passages from the website/github and interpret them in a way that fits your view. I read them and I interpret them in the opposite direction. The problem BIP110 addresses is severe enough to tighten the rules significantly but not to the point they break the foundations. In fact they reinforce them. Ironically the top down decision making of Core v30 made this fork necessary not just in principle but in practice. If you don’t know what I talk about it maybe you haven’t paid enough attention, or you simply prefer to think it’s a nothingburger. Maybe you should have applied this higher standard towards protocol development to Bitcoin Core too. Did you? Are you running v30? If not, why?

I am opposed to core v30 for the exact same reasons I am opposed to BIP110: sloppy engineering forced through the community with poor arguments.
Btw, core v30 didn't enable posting contiguous harmful content on chain: it was enabled in 2013 by OP_RETURN, that was limitless at the consensus level from the start. And to be clear, the threat was well known all along. There are press articles from 2018/2019 that were FUDing about it during that bear. Anyone who's familiar with bitcoin, like Luke also is, has knew about this for years if not a decade — so why is it suddenly an emergency after all that time? Core 30 sucks and it shouldn't have happen - but it is simply not true that it made that attack viable, and anyone who thinks so is deeply miseducated about how bitcoin works.
All of this is just ego war and people wanting to feel great about themselves. If the priority was to protect bitcoin against this attack, then capping OP_RETURN size would have been enough, and much much more likely to pass. But ofc they had to overdo and turn this into a personal vendetta, and now the chances of fixing the actual important thing by the end or the year are 0.
Good, so we can establish a baseline around v30. I’m aware contiguous data isn’t new. The difference is that it wasn’t a systemic problem until the 2023 inscriptions exploit. Before that, large-scale data stuffing required convoluted workarounds and remained marginal. There wasn’t a real economic split between monetary and non-monetary use at scale.
What changed wasn’t the code alone, but the incentives. Once a market formed around inscriptions and it became culturally normalized, the behavior scaled aggressively. The data reflects that shift. At that point, it stopped being edge-case experimentation and became an industrial use of blockspace for non-monetary payloads.
Uncapping OP_RETURN without first addressing the underlying inscriptions vector only amplified the issue. It expanded one data pathway while leaving the more structurally problematic one untouched.
Are you familiar with the mechanics of the inscriptions exploit? Or how it was handled in 2023? Understanding that context clarifies much of what followed with Core v30 and why BIP100 focuses not only on OP_RETURN but also on alternative data embedding methods. What looks like an overkill is actually trying to patch a leaking bucket with many holes.
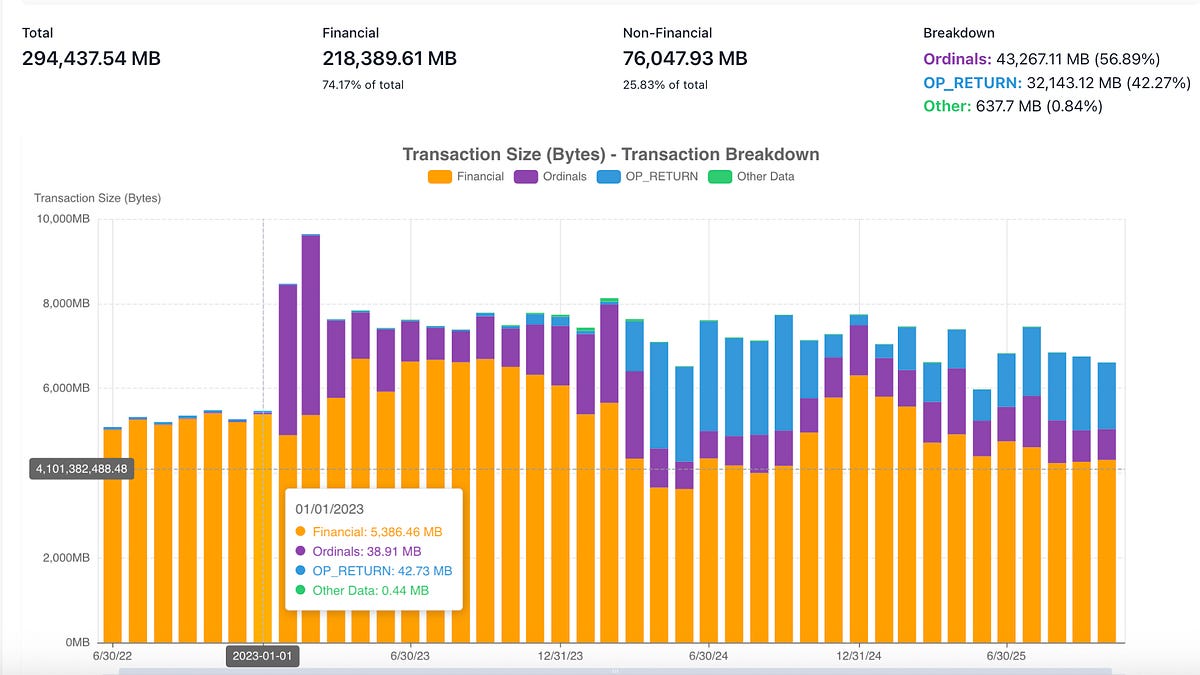
Issue #3 - Three Years of Spam
From zero to 36%: a timeline
Wow, that's a great response to his questions.
It shows that you might be compromised in some way. I hope you can get out of the swamp.
I'm familiar with this but either ways the facts are not siding with the idea of an emergency. Most ordinal projects are dead, investors are ruined, and tx fees have been ridiculously low for months.
Besides, you are conflating two very different issues, just like BIP110 is doing. Capping OP_RETURN, which has outlived its utility, to protect nodes from hosting contiguous illegal content is arguably very important. Dealing with witness-embedded spam is secondary and optional. Witnesses can be pruned away, and it's not even sure jpegs are coming back. The were economically viable just because of a hype that is long gone and, would it come back, unsustainable by nature.
As I said, by trying to achieve aggressively everything at once, this BIP is not only harmful to legitimate monetary projects lead by genuine bitcoiners, it's also condemning itself to fail, missing an historic opportunity to fix a long-standing vulnerability.
This data disagrees with your lax view on spam abuse. That’s why I included the link in my previous post. Might be a good idea to give it a read, although you seem convinced your POV is infallible, so there might be no point in trying to convince you more.

Well once again if you cap op_return, that leaves only witness-embedded spam that you can prune away. Your graph actually confirms that it doesn't amount to much, so I'm pretty confused about how you're reading it? The point is, we could have gotten rid of that op_return part with a simple, consensual fix but instead they wanted to push it too far to prove something, and what'll we get is no fix at all because this thing is crappy and won't activate.
Agreed that this is not ideal and its a risk on bitcoin stability (assuming the BIP-110 fork is initially a minority chain), but in your opinion, what should we do about UTXO bloat (which is a risk on decentralization) ?
A change to the consensus rules of bitcoin. The rules that say whether a transaction is valid and can be added to a block.
Or was that not your question? Any sarcasm here went straight over my head 🚸
Primary consensus rules (in plain English)
- Bitcoin Controlled Supply Rule - Total supply of Bitcoins is controlled to a fixed number of 20,999,999.9769 Bitcoin.
- Bitcoin Mining Reward Rule - How many Bitcoins are rewarded to the miner who creates a new Bitcoin block from the coinbase.
Bitcoin Proof of Work Rule - The block hash must meet the cryptographic difficulty requirement.
- Each Bitcoin transaction input must have the correct signature of its address owner.
-Each Bitcoin transaction input can only be used once in the Bitcoin block.
- Each Bitcoin transaction must be in the correct data format.
- Each Bitcoin block must be in the correct data format.
- Each Bitcoin block must contain the hash of the previous block in the blockchain.
I am being pedantic but, my point was that nothing was "changed" persay. BIP 110 added rules and did not change the previous consensus rules.
It would be fair to say "Only one side is pushing stricter rules for consensus"
Adding a rule is changing the rule set, by most people's meaning of the words. But there is a slight difference. I shall endeavor to be clearer in the future.
But my point stands, one side is trying to rush through a change in the consensus rule set by adding new rules.
My main problem is the rush. That reeks of scammers trying to make people make mistakes by acting emotionally. Also the "temporary" part is just not sound money.
I completely agree about the Flag Day activation, completely unnecessary. If people want the software, then they can run the software. No need to put a timeline on it. Spam is a slow death that builds up.
But I don't see temporary as a negative. It seems like a compromise in an attempt to find a better solution that is less restrictive for innovative usecases.
I don’t care if it’s prunable or not. It makes running a node harder anyway. If the previous screenshot wasn’t clear, I hope this one is.

I think putting a hard cap on OP_RETURNs would be the single best non-risky thing to do. However, I think bitcoin adoption will cause blocks to be mostly full a few years from now - and the fees to be much higher. So it would only buy some time & avoid harmful content onchain.
It just shows that 80% of the bloat nowadays comes from OP_RETURN, as I already explained. You really missed the point on that one.
Btw, just a few years from now, our blocks will be systematically full of monetary transaction because of adoption. Do you think it will cause bitcoin to collapse, or to the least to centralize completely? Or, in your view, are non-monetary transactions the only ones that can cause a node to struggle? Because if full blocks are a threat to bitcoin, then mass-adoption is a threat to bitcoin too, isn't it? Then maybe we should make sure Bitcoin never expands and never growths, just like BIP110 proposes... :)
I agree that financial transaction will likely price out most of the spam in the long term, and block size are static so no storage issue, but the problem isn't there, the problem is in the UTXO set, which inscription such as ordinal creates multiple non used UTXO which nodes need to keep in RAM (so RAM cost are going significantly higher, so node cost more overtime. So I believe one of the most important things is to remove at the consensus level exploit that permit inscriptions to save UTXO set (which is what BIP-110 is mostly doing) now is BIP-110 the good approach, maybe not but at least its working in the good direction.
I haven’t missed anything. The graphic just shows that:
a) when you have two buckets, spammers will abuse both.
b) if you close one, they’ll switch to the other, so you need to close both.
c) fees can’t outprice spam, bc there’s infinite demand for free data storage
> our blocks will be systematically full of monetary transaction because of adoption
Good, that’s the whole point of the debate: save the 36% space used by spam to accommodate more financial transactions. In this regard BIP110 is a de facto scaling solution.
Not if both buckets are already full... Also it's not free if there's a fee 🤔.
Anyway, I don't need to be convinced that spam is a bad thing. My point was that preventing contiguous harmful content onchain should be the priority for obvious reasons. But I think I already went over my point extensively so probably we should stop here?
Agreed
Why can't fees out price spam.. Has anyone done the numbers on this? Do minimal fees eliminate more than 95% of the spam?
Some thoughts from another post:
 umni
Should we be fixing a problem before it has arrived? How can we accurately define the problem if it isn't here yet? (high on chain fees) are their consequences to fixing problems that currently don't exist?
Is it ever possible to define "honest party"?
"so our collective goal is to keep transactions off chain as much as possible"...
Aren't high fees the only thing to incentivise this, the literal pricing mechanism and tampering with the pricing signals gets us into some serious trouble? Look to any of the unlimited historical examples.
Would you agree it might be possible to remove too many transactions off chain? What would the result look like if so....
If you look at Bitcoin alone you might think it is dying, similar to an old tree being overtapped, transactions representing its the flow of sap, and spam representing the buildup of moss or fungi.
On chain fees are a measure of how much off-chain transactions could take place before damaging the underlying chain. If we see 'subjective' spam appearing on chain, maybe we overtapped the tree... maybe we're killing it. Instead of manually removing the moss or fungi build up with bip110 we should on chain some transactions and aggressively discouraging bitcoin derivatives socially.
1 solving problems before they arrive.
2 creates new problems, spam.
3 solve for new problem, setting precedent by defining spam externally. Instead of using pricing incentives the only real spam filter
Looks a lot like the beginning of a negative feedback loop or governmental growth.
"Never attribute to malice that which is adequately explained by "good intentions"."
I agree with every one of your points but it is the consequences I am afraid of. As we're all aware we can't plant another tree.
View quoted note →
Honnestly I think it's hard to generalize the answer, because the non-monetary market oscillates between two states: hyped or dormant.
Hyped markets, such as during the inscription craze, can actually outprice monetary usage & that's precisely what caused all the resentment against these use cases - they are also incredibly hungry in block space and significantly deter scaling efforts, on a system that is already low throughput. Luckily, this state isn't sustainable - it's a bubble - but it's definitely a nuisance.
Dormant markets can definitely be outpriced, though the UTXO clutter and block burden from the past doesn't go anywhere, right? What's happening right now is that, because onchain activity is so low, miners will fill the blocks with whatever garbage at whatever price - which is always better than 0. In other words, for miners, there's always an incentive to fill the blocks no matter what. This is why I think we entered an era of forever-full blocks, because miners can now marginally stimulate markets that will buy the stranded block space for storage or meme.
This whole thing gives the statistical illusion that spam has been able to constantly occupy a significant portion of our blocks, and that it will be able to keep doing so; But that's conflating two different states of the market. In the first state, it was a real nuisance because it was outpricing bitcoin users, clogging the throughput. In the second, current state, it's not outpricing anyone, it's just that bitcoin is not being used at full capacity. Arguably, the spam market is now so weak that we could easily outprice it if more people were to use bitcoin - it's not clogging the throughput anymore, but it is definitely filling the blocks, adding unecessary weight to the blockchain.
My point in an earlier note was that, whether or not you manage to defeat that spam, it won't take long before the block fills again durably because of mass adoption. Either way, forever-full block is a state of things we'll have to adapt to. Now, if we could dodge another spam hype or two, that would definitely be a great thing — but doing so through a BIP that hurts bitcoin fundamentals & legitimate projects is definitely a bad trade.
Good engineering requires to be level-headed, patient, focused, and be willing to look at the problem from as many angles as possible in orders to discover the best trade-offs. Only the highest quality solutions should be allowed to make their way into bitcoin consensus. There's a reason why most proposal fails, and it's a very healthy state of things. :)
Pathetic. How about doing real debate instead of spreading BS?
Thanks much for an understandable, sensible, non-emotional explanation. I'd zap you some coin but ran into all kinds of kyc hurdles trying to use primal wallet and others here on nostr - but that's another can o worms.
HEY DO YOU STILL HAVE ANY COLDCARD PROMO CODES?