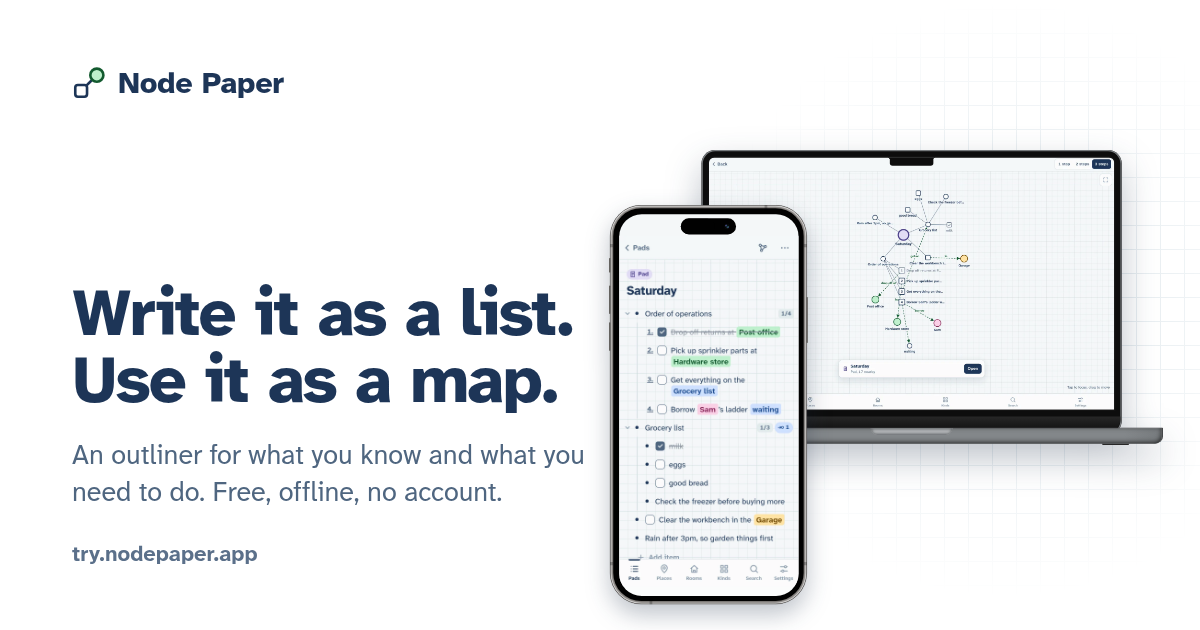
I made this for me, but it might be good for you: use the open source web/PWA version for free forever, or toss a few sats my way for multi-device sync, authenticated and e2e encrypted with your nostr keypair. Send me your questions or feature requests!
Replies (11)

I need to play around with it more, and maybe toss a clank at it to review security claims... I'm also curious how it does data storage, as I worry I'll lose things if I don't take care to back them up somehow (where is it saving stuff? How do phones work?! I'm very ignorant). If it passes my (AI's) scrutiny, may buy a sub :)
@Gigi you might be interested in yet another note taking app, as I think you're something of a super user
definitely do your own research on security! quick answers: - data is stored in your browser's local storage, in a local database. - if you are using sync (either the hosted version or running your own server) the app syncs the encrypted bullets and metadata to a server. updates are pushed out to all devices, the data is decrypted on the device, in the browser. - if you're not using sync, you _would_ lose all your data if the browser cleared its data. there's an "export" button in the settings that dumps your entire database as .json in a way that it can be "imported" back again later.
I see. On phone I have no idea how it's storing. On desktop I got a prompt about local storage, but wasn't familiar with this behavior from a website before. When using sync, should I be worried the server owner could read my notes? If I really started using this heavily, I'd want to store lots of details I consider private. You don't have to answer all this, just what's on my mind, that I may ask AI about later
ask away! there are some different storage and security model details between devices, but in general "the browser is always storing it locally" - even if different devices or OSes prompt for approval and whatnot in different ways. "service workers" is the thing you'd want to talk to AI about. There's literally nowhere else for the data to be - if you haven't signed up for sync, there's nothing of yours on a server anywhere. your browser loaded the client code and is doing everything on-device. (you could prove this to yourself by opening the site on a new browser and killing your network connection. then write some stuff and refresh. it'll still be there). on privacy: if you use sync, the data is encrypted client-side using a nostr keypair (doesn't have to be your real npub). only the holder of that nsec can decrypt the data. but yes: a security review by an agent would make you feel better. If you get a good report before me, I'd be happy to add it to the docs!
I'll give it a whirl a bit later, just for kicks. Am curious, why nostr key pair over say some other method (PGP maybe, not sure..)? Is there a benefit to the Nostr-specific design I'm unaware of (more efficient curve maybe)?
good support for client-side signing, remote signers, well-documented protocols for all the things this app needs. also: was planning on introducing it to this audience, so a "bring my own login" feature is a nice bonus. ....also also...: there are sharing features on the roadmap ;) sending graph subsets to friends. working on a shared list together live... it'll work exactly like multi-device sync, except some of those devices are other npubs. for isolated data that you control sharing for, of course.
↑