Dark Web Informer :verified_paw:'s avatar
Dark Web Informer :verified_paw:
DarkWebInformer@infosec-exchange.mostr.pub
npub1xcpw...hx5s
Website: https://darkwebinformer.com Website Pricing (Crypto payments are fully automated): https://darkwebinformer.com/pricing Socials: https://darkwebinformer.com/socials API Access: https://darkwebinformer.com/api-details About Dark Web Informer: https://darkwebinformer.com/about-dark-web-informer X: https://x.com/DarkWebInformer Updated: 2026-07-20
⚠️ Disclaimer: This video explores disturbing allegations, unsettling online behavior, and sensitive subject matter involving minors. smartschoolboy9: An Internet Rabbit Hole In April 2024, a Reddit user uncovered a disturbing collection of Instagram accounts that appeared to be operated by children. But a closer look at their unsettling content raised serious questions about who was really behind them and what was happening out of sight. What followed was a descent into one of the internet’s most bizarre and disturbing mysteries: smartschoolboy9, a rabbit hole that continues to raise questions to this day. Video Credit: youtube.com/@NickCrowley
🚨🇺🇸 Hackers target Federal Election Commission, forcing filing system offline The U.S. Federal Election Commission temporarily shut down its electronic filing system after hacking attempts disrupted the service one week before the November 3 midterm elections. ⠀ The outage prevents political committees and other organizations from submitting mandatory 24-hour and 48-hour spending reports, reducing the amount of current campaign-finance information available to the public. ⠀ The system has reportedly been offline since around 10 p.m. ET on October 26. FEC staff are working to restore the service, while previously filed reports remain searchable on the agency’s website. ⠀ There is currently no confirmation that the attackers gained access, stole data or altered any filings. The identity and motive of those responsible also remain unknown. ⠀ The FEC tracks campaign spending but does not administer elections. The incident should not affect voter registration, ballot systems or the public’s ability to vote. Source: https://www.reuters.com/technology/hacker-trying-breach-us-federal-election-commission-system-email-shows-2026-10-27/ image
🚨 Kali Linux 2026.3 released with Linux kernel 7.1.5, new tools and major NetHunter updates The release refreshes Kali’s image-building scripts with consistent options across platforms and adds support for building inside Docker or Podman containers. ⠀ Kali 2026.3 also introduces KDE Plasma 6.7, 126 package updates and six new tools: • dalfox • katana • qsreplace • rustscan • sdrangel • snaffler-ng ⠀ NetHunter now supports wardriving from TicWatch Pro 3 devices, phone-based control of NetHunter watches, NFC card operations and KernelSU. Source: image
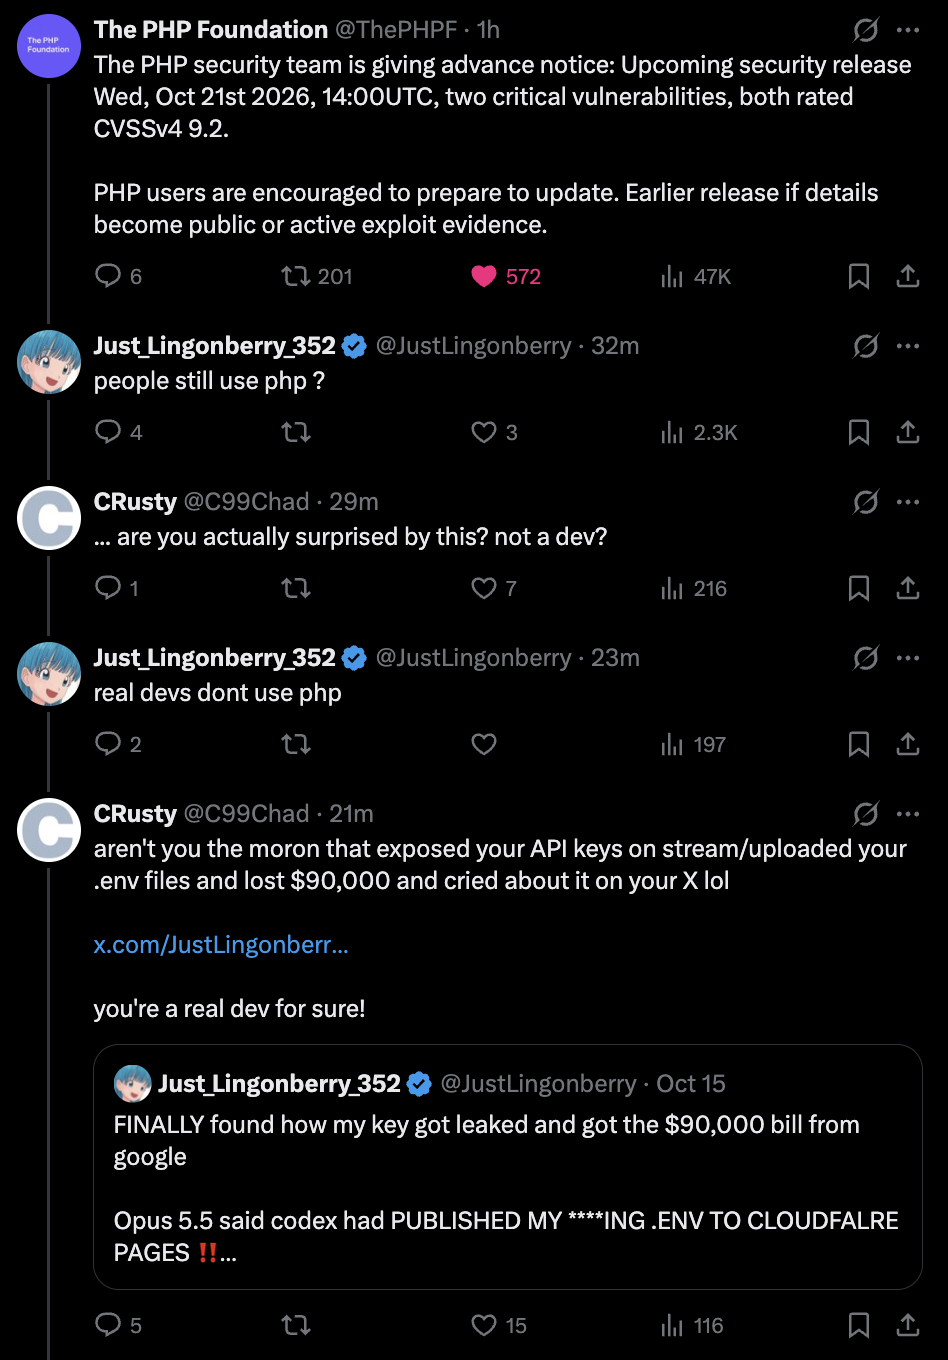
🚨 PHP warns of two critical vulnerabilities as emergency patches arrive tomorrow The PHP security team will release updates on October 21 at 14:00 UTC for two vulnerabilities, each rated 9.2 under CVSS v4.0. ⠀ Security researchers identified the flaws as CVE-2026-109618 and CVE-2026-109619 and described them as remote code execution vulnerabilities reportedly affecting PHP versions 5 through 8. PHP has not yet confirmed the affected versions, exploitation requirements or fixed releases. ⠀ The vulnerabilities were reportedly leaked before their planned disclosure. Researchers said they have not observed active exploitation, while PHP warned it may release the patches early if technical details become public or exploitation is detected. ⠀ Administrators should identify PHP installations now and prepare to apply the updates as soon as they become available. Source: image
🚨🇬🇧 Dark web child r*pist identified through lingerie photos and images of his hands jailed for 23 years Darren Welsby, 48, was convicted of r*ping and sexually abusing children, some as young as six, and recording and distributing the abuse online. ⠀ Investigators traced Welsby after the username “wellhnug,” used to upload child sexual abuse material on the dark web, was also used on an adult website where he posted photographs of himself wearing women’s lingerie. ⠀ A forensic anthropologist then matched his hands and knuckles to those visible in the abuse images, while digital experts established that the material was captured using one of his phones. A search uncovered more than 30,000 abusive images across 10 devices. Welsby was sentenced to 23 years in prison and will serve a further five years on extended licence. Source: image
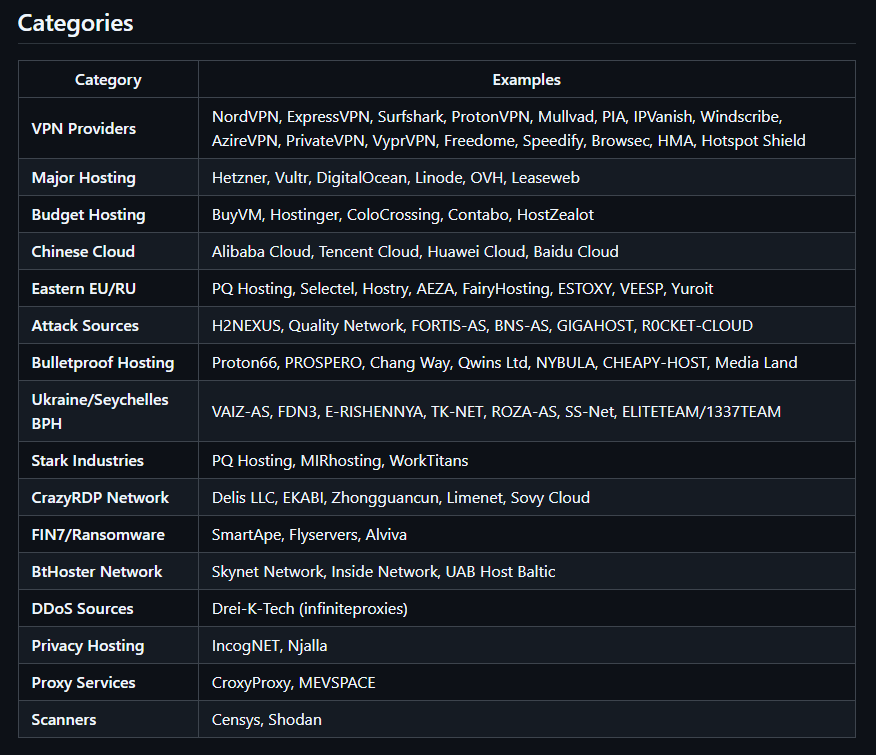
🚨 Bad ASN List: A curated blocklist of 2,200+ ASNs tied to VPNs, datacenters, hosting providers, scanners, and infrastructure commonly associated with automated abuse. GitHub: The list is designed to help reduce scraping, credential stuffing, bot traffic, anonymous abuse, and other unwanted activity by identifying suspicious network sources at the ASN level. Includes categories covering: • VPN and proxy providers • Major and budget hosting • Bulletproof hosting • Known scanner infrastructure • DDoS and abuse sources • Infrastructure linked to ransomware and cybercrime activity The repo currently contains 2,234 ASNs and includes implementation examples for Cloudflare Workers, Node.js, Flask, iptables, and nftables. image
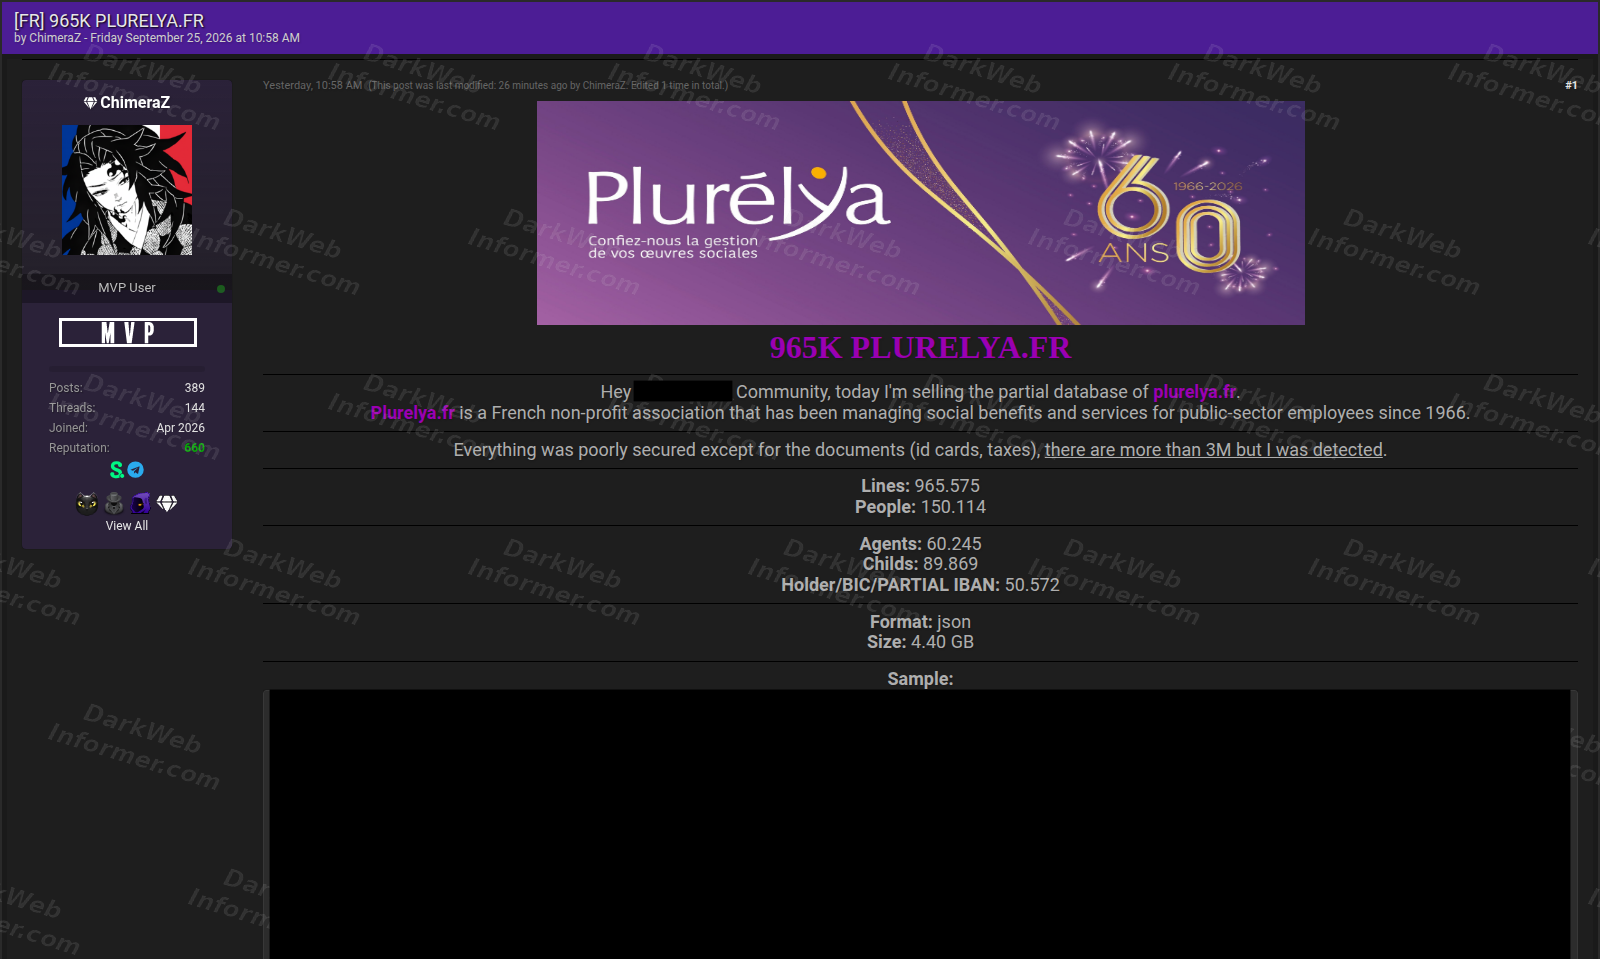
🚨 🇫🇷 Plurélya dataset containing public-sector employee and family data offered for $250 ⠀ The actor "ChimeraZ" is selling what they claim is a partial dataset from Plurélya, a French nonprofit that administers social benefits and services for public-sector employees. ⠀ The 4.4 GB JSON archive is advertised as containing 965,575 lines associated with 150,114 people, including 60,245 employees, 89,869 children, and 50,572 records containing account-holder names, BICs, and partial IBANs. ⠀ Samples include names, dates of birth, personal email addresses, home addresses, employment details, internal identifiers, tax-related fields, and records linking employees to their children. The dataset is being offered for $250, payable in Monero. ⠀ The actor also references more than three million identity and tax documents but claims they were detected before obtaining them. It is unclear whether any of those files were accessed or exfiltrated. ⠀ This claim is currently unverified. ⠀ 💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
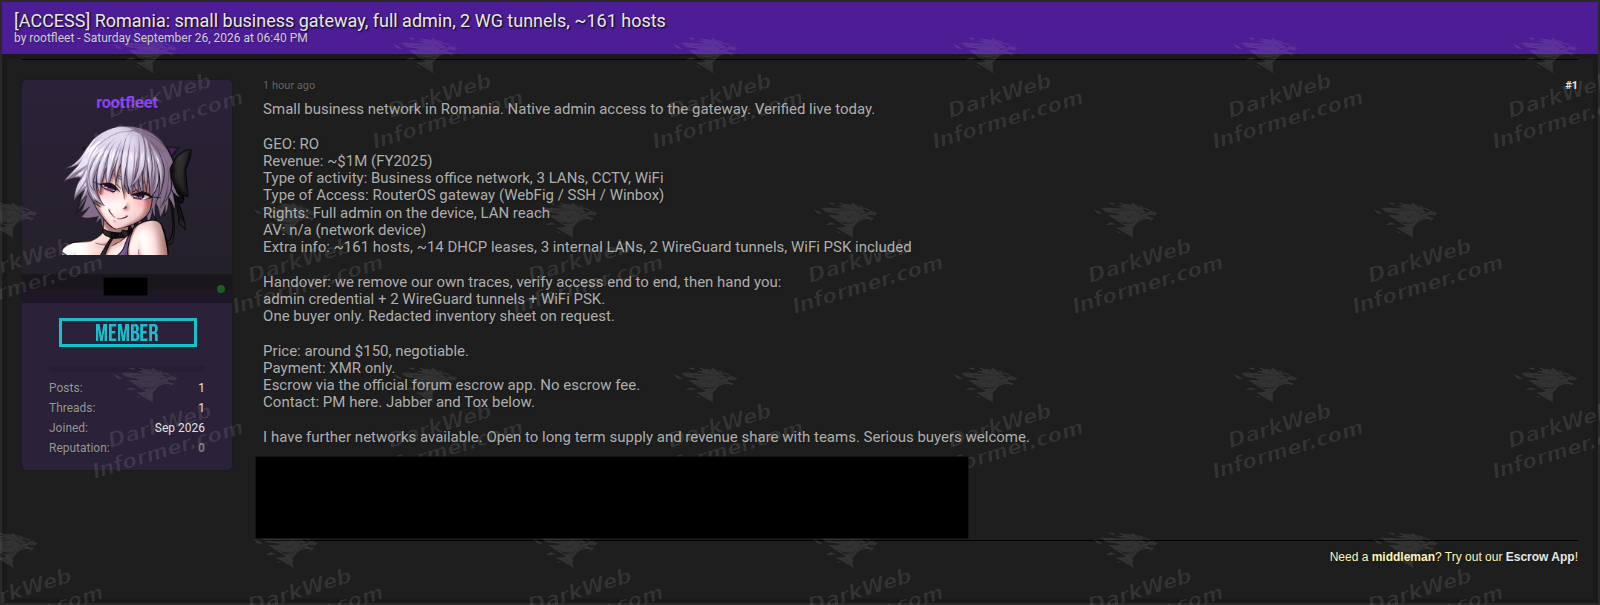
🚨 🇷🇴 Initial Access: Romanian Small Business Network A threat actor is advertising administrative access to an unnamed Romanian business network reportedly generating approximately $1M in annual revenue. The advertised access includes full admin control of a RouterOS gateway, three internal LANs, two WireGuard tunnels, WiFi credentials, and network reach across approximately 161 hosts. The access is listed for around $150 in XMR. This claim is currently unverified. 💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing image
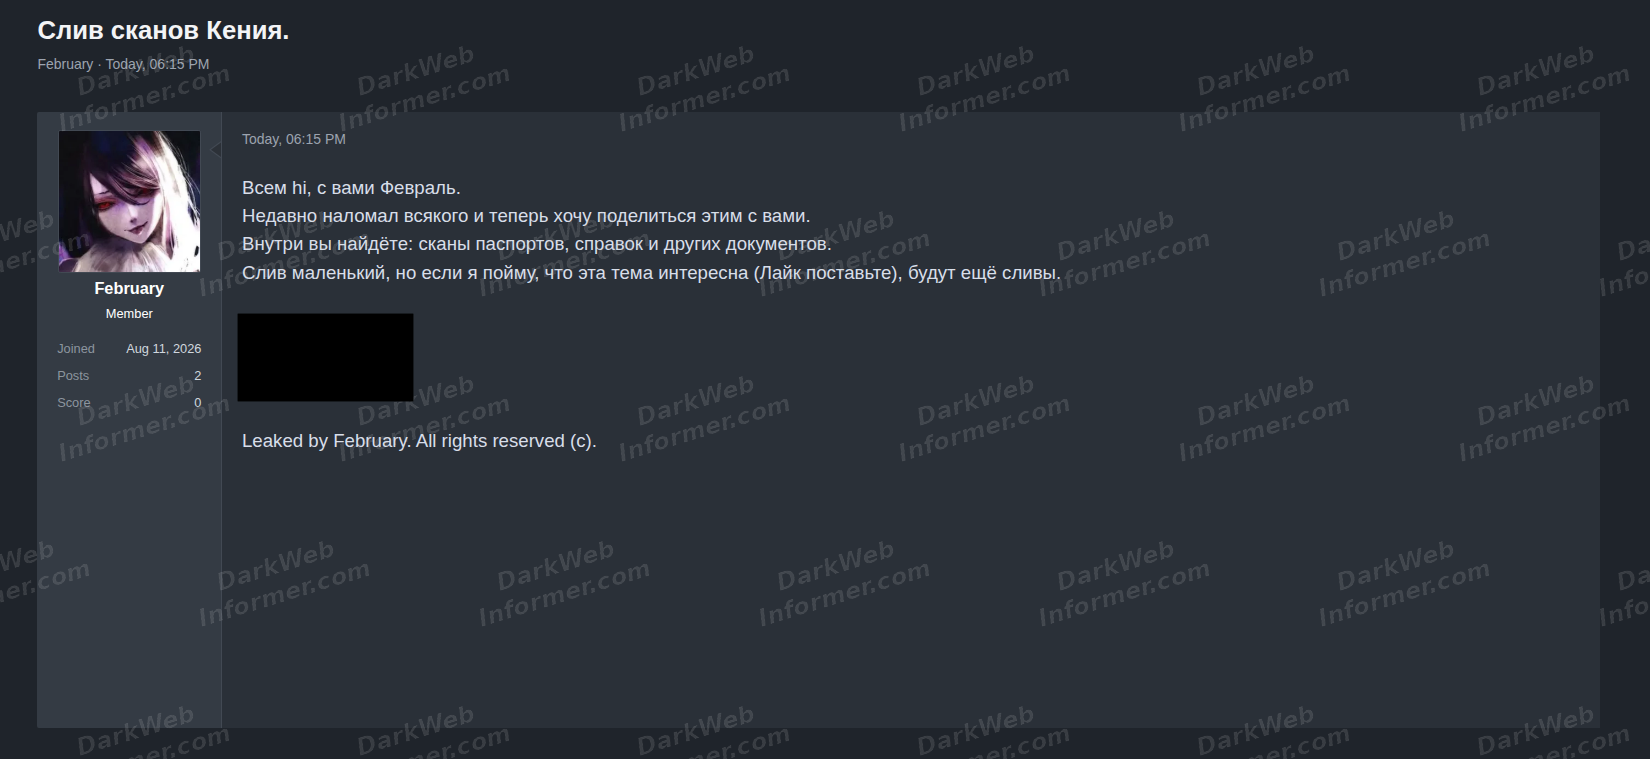
‼️ A forum actor known as February shared scanned passports, certificates, and other documents allegedly obtained from Kenya, distributed for free. The poster indicates further leaks may follow depending on community interest. image
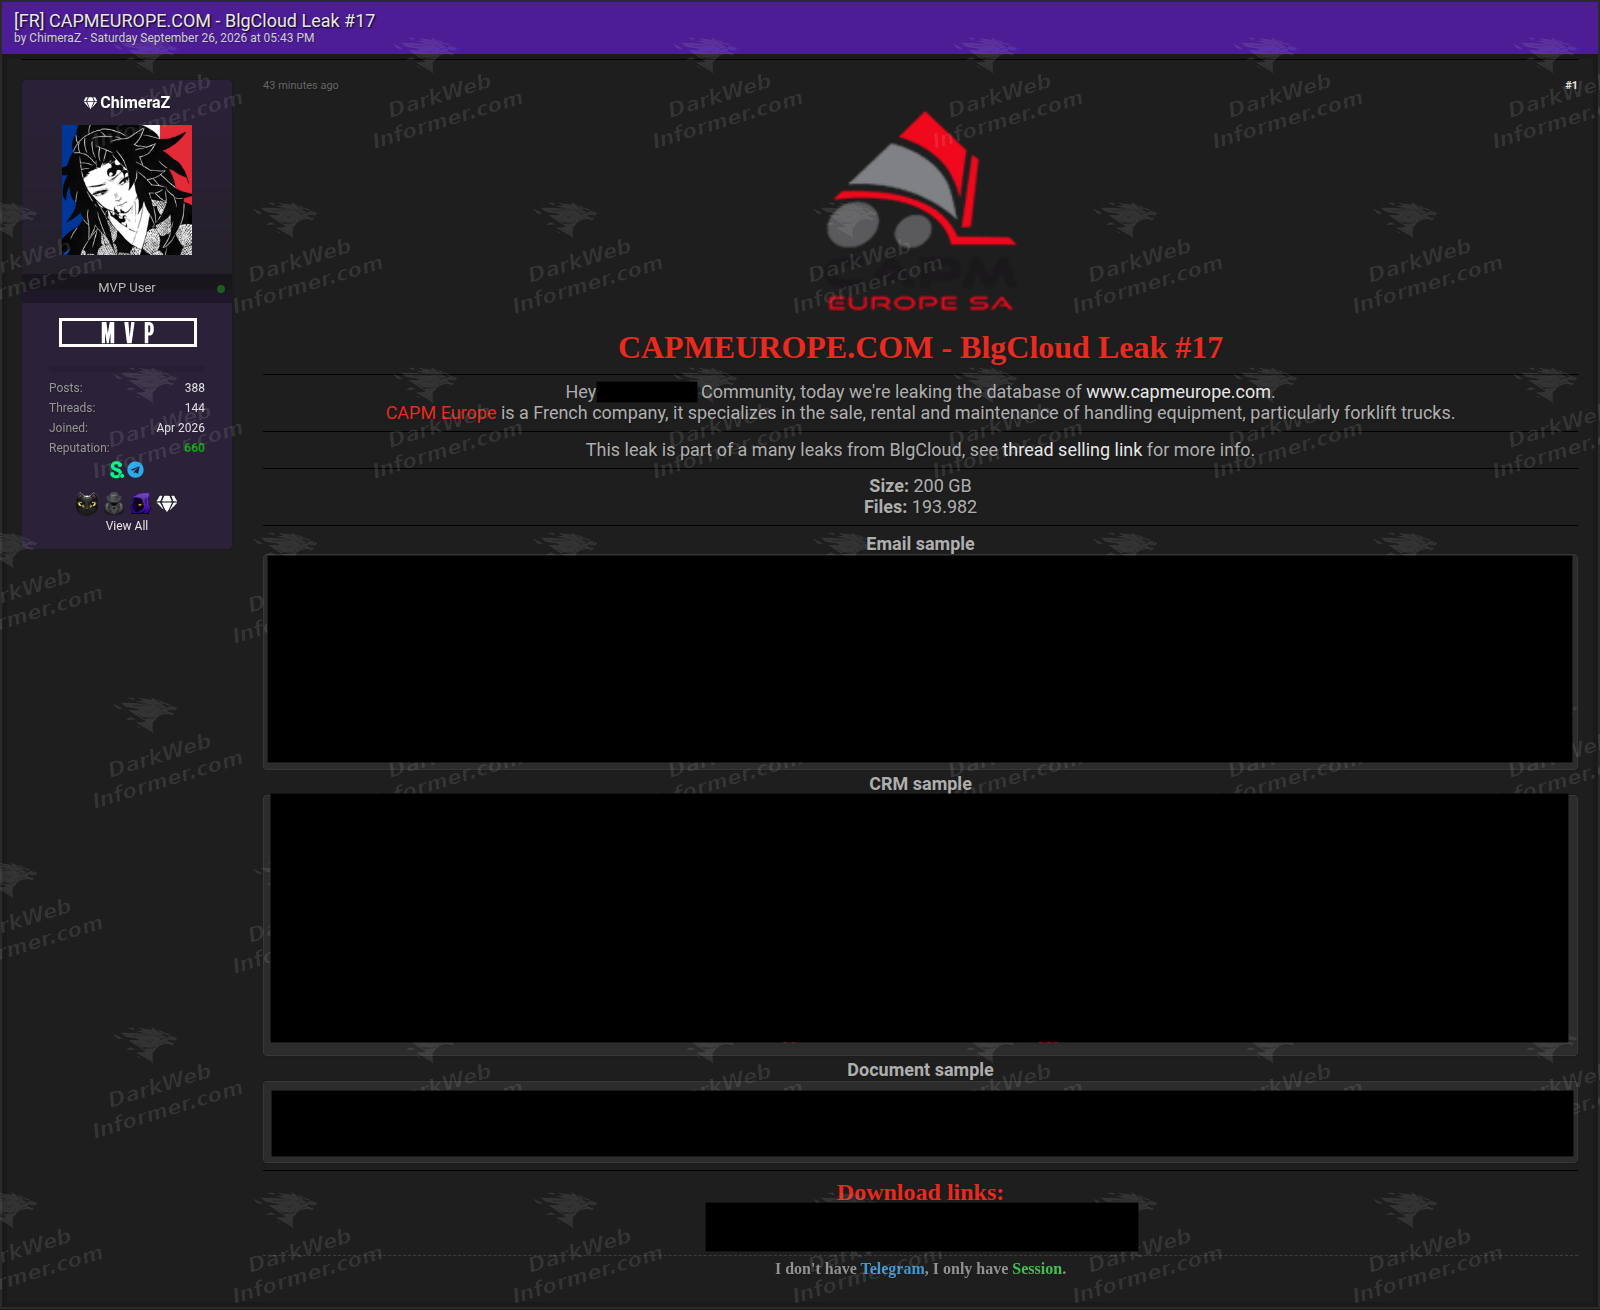
🚨 🇫🇷 200 GB of CAPM Europe data allegedly released in BlgCloud leak series ⠀ The actor "ChimeraZ" has posted download links for data allegedly taken from CAPM Europe, a French company specializing in the sale, rental, and maintenance of forklifts and other handling equipment. ⠀ The archive is advertised as approximately 200 GB containing 193,982 files. Samples shared in the post reference company email, CRM records, and internal documents, including employee and customer contact information, account records, addresses, and document metadata. ⠀ The release is labeled "BlgCloud Leak #17." The post does not explain how CAPM Europe was compromised or when the data was obtained. ⠀ This claim is currently unverified. ⠀ 💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing image
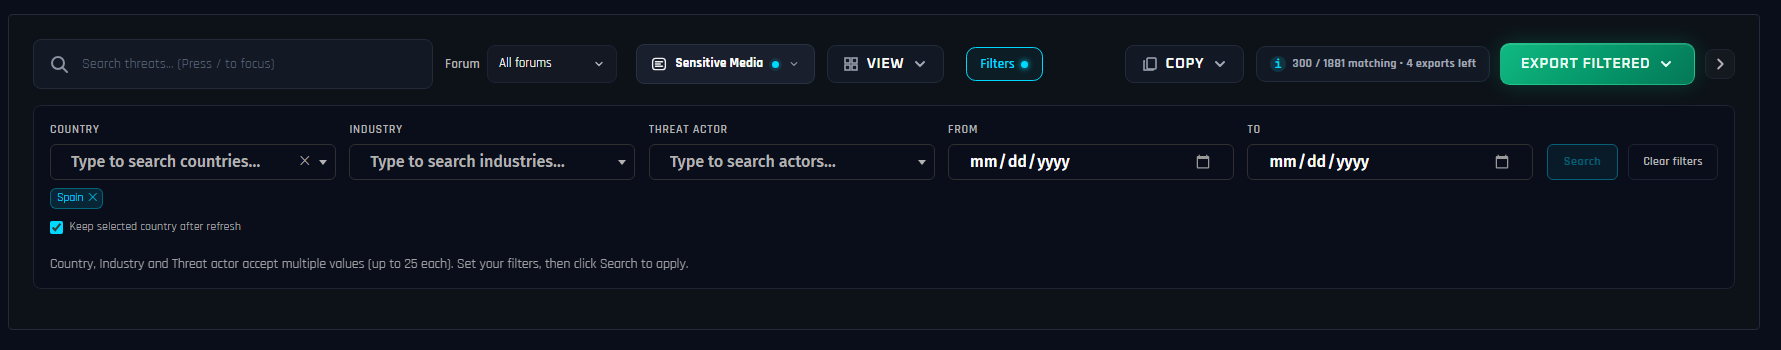
Small Threat Feed update: You can now choose to keep your selected country filter after refreshing the page. For example, select Spain under filters, enable “Keep selected country after refresh,” and it will automatically be restored before the feed loads again. Changing the country updates the saved preference, while clearing filters removes it completely. Also works with multi-country filtering. Refresh the page to get the update. image
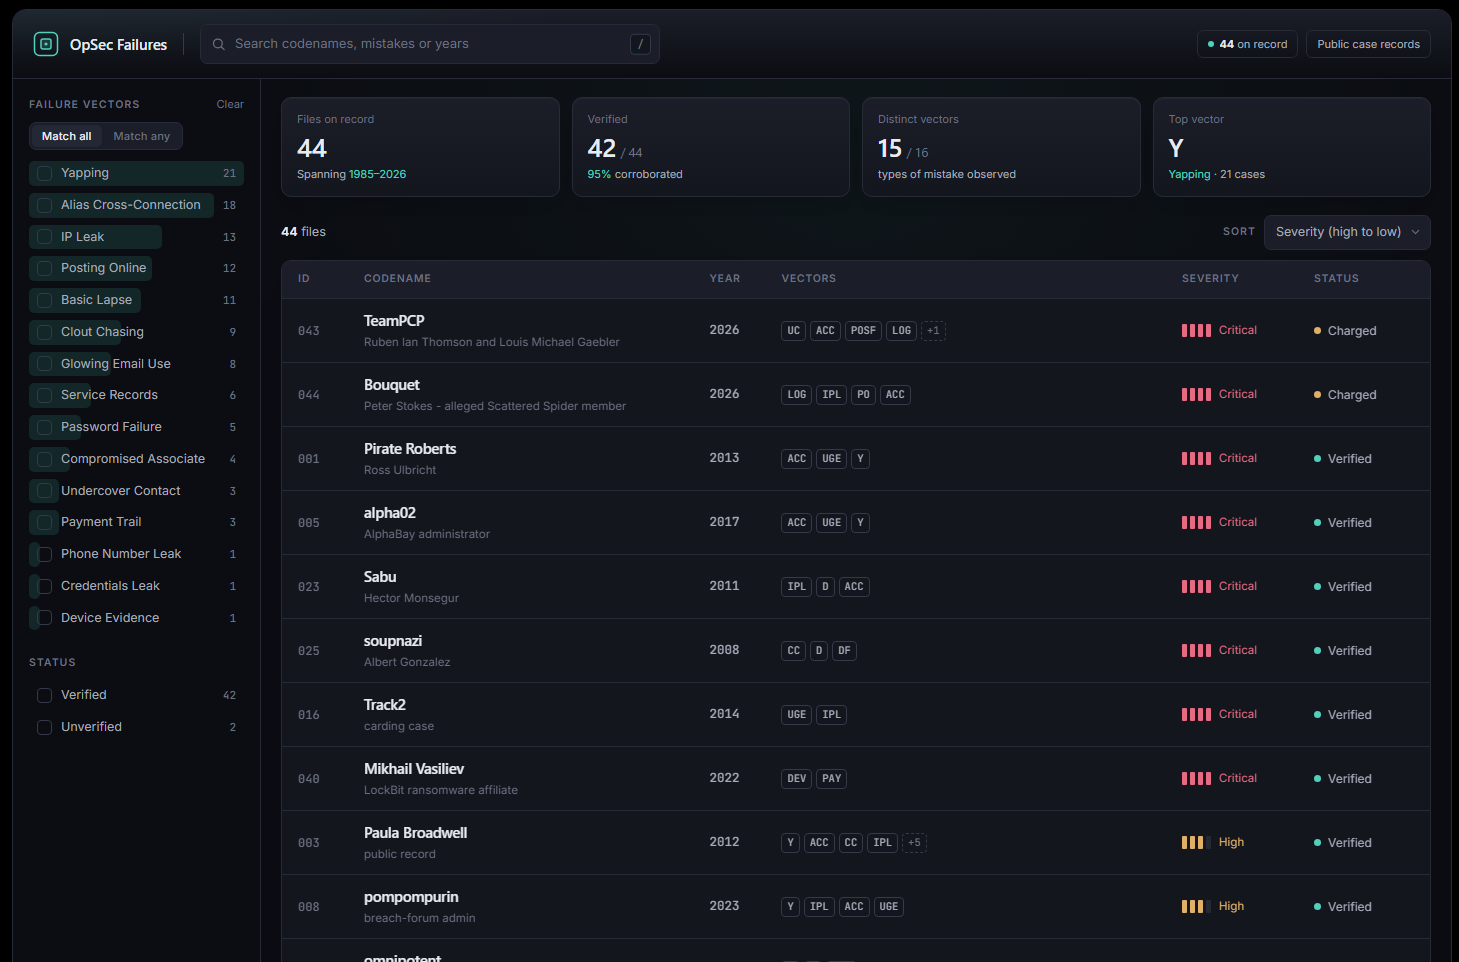
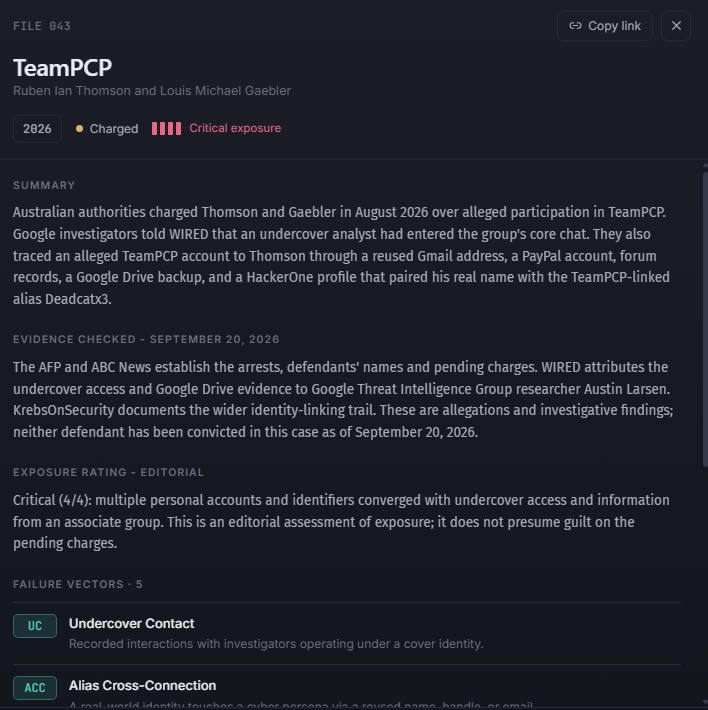
Getting closer to releasing the OpSec Failures page. A couple things I'm working on still. Should be out next week. Things like legal documents, when known, will eventually be added to each individual. There will be a submission button somewhere as well... so you can submit new individuals, new info, provide updates on some things that may not be entirely correct, etc. Again, no paid subscription required.
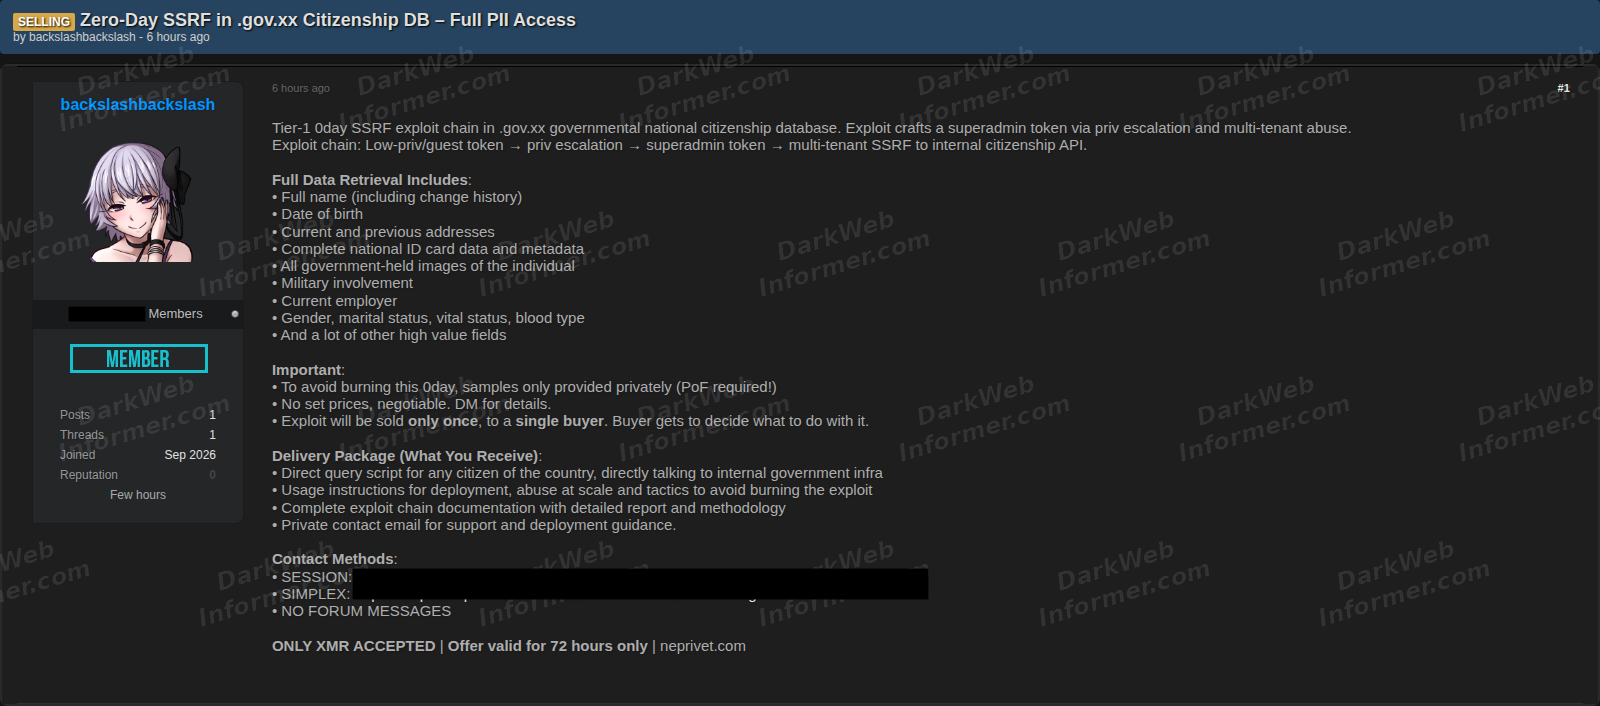
🚨 Government citizenship database zero-day access allegedly offered for sale A forum actor using the handle "backslashbackslash" claims to be selling a zero-day SSRF exploit targeting an unspecified government citizenship database, which the actor says can provide privileged access to citizen records. Claimed accessible data includes: ⠀ • Full names and name-change history • Dates of birth • Current and previous addresses • National ID card data and metadata • Government-held photographs • Military involvement information • Employer information • Gender and marital status • Vital status and blood type ⠀ The actor claims the exploit can provide broad access to records for citizens of the affected country and says technical samples will only be shared privately with prospective buyers who provide proof of funds. The listing states the exploit will be sold to a single buyer, accepts XMR only, and says the offer is valid for 72 hours. The affected government and country are not identified in the public listing, and the claim is currently unverified. ⠀ 💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing image
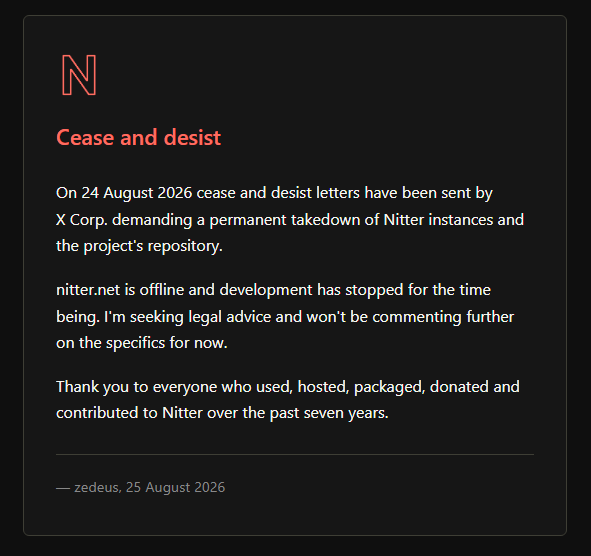
🚨 Nitter development has stopped after X Corp. sent cease-and-desist letters demanding the permanent takedown of Nitter instances and the project’s repository. The maintainer says nitter.net is now offline while legal advice is being sought. Nitter had operated for more than seven years. image
↑