Tailscale SSH Flaws Could Let Hackers Gain Root Access Across Servers From One Compromised Device
https://cybersecuritynews.com/tailscale-ssh-flaws/
Wilder
wilder@cypherpunk.today
npub15xkp...krnh
Cryptoanarchist, voluntaryist, perpetual traveler focused on technology and society hacking.
Slovensky análny masterpiece https://npub1vua9wgmrjn70t3awszeea6zlxjf6dh8g7cm0ayeumr4rx4ffr3mqqvhtf9.nsite.lol/
At the (last) LABITCONF 2026, I'll have the presentation:
Disruptive crypto / AI: Giving back the digital freedom that state and bureaucrats are taking from you.


Pavol Lupták — LABITCONF 2026
Liberation.Travel
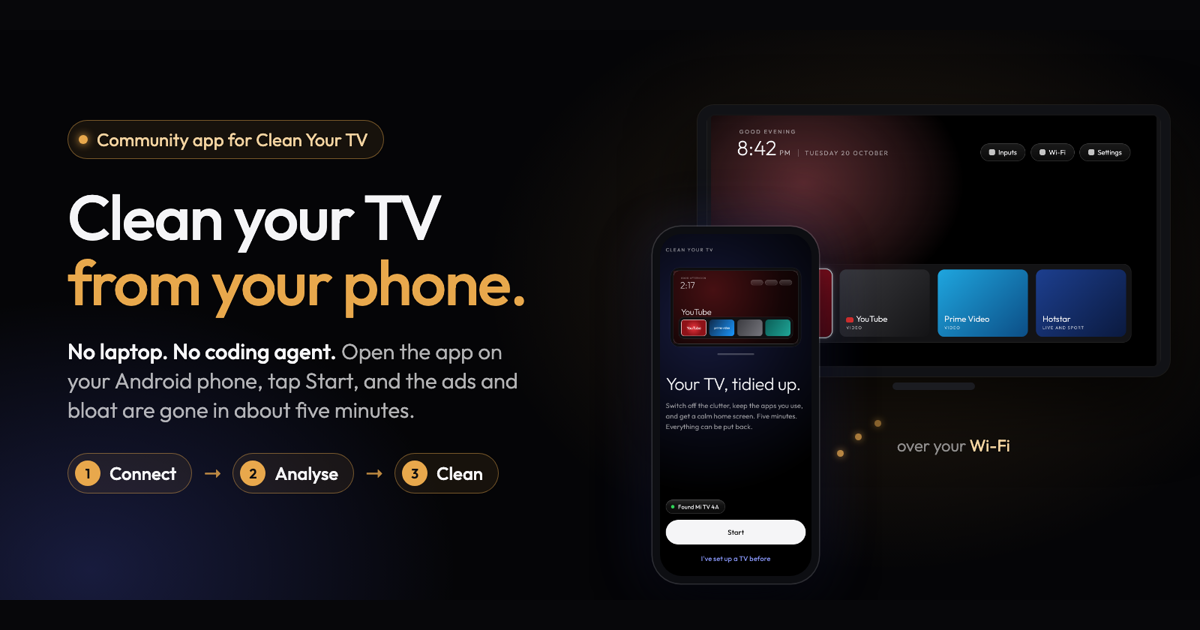
Clean your TV from your phone
No laptop. No coding agent. Open the app on your Android phone, tap Start, and the ads and bloat are gone in about five minutes.


CleanYourTV
Community-built phone app for Clean Your TV
A community-built phone app for Clean Your TV: clean up your Android TV or Google TV from your Android phone over Wi-Fi. No laptop, no coding agent...
Dessa model trained on audio only. Previously speech to text to llm to generate answer then convert to speech again.
Dessa skips all of this and produce natural answer.
Dessa - the Conversation Model trained only on speech
You learned to talk by listening. So did Dessa. A research preview of a full-duplex speech model.
codr connects coding agent sessions in herdr to White Noise, with one encrypted chat per session. Send a message from your phone to continue coding, create a project, choose an agent or model, and read the replies in the same chat.

GitHub
GitHub - tidley/codr: Encrypted White Noise chats for local herdr coding agents. Primary source, issues, PRs, CI and releases: https://github.com/tidley/codr. Independent ngit mirror linked below.
Encrypted White Noise chats for local herdr coding agents. Primary source, issues, PRs, CI and releases: https://github.com/tidley/codr. Independen...
The End of the Easy Plan B: Latin America Now Wants Your Capital or Your Time
Latin America increasingly wants capital or time. For a Plan B without relocating, investing is now the way in, David Lincoln argues.


IMI Daily
The End of the Easy Plan B: Latin America Now Wants Your Capital or Your Time - IMI Daily
Latin America increasingly wants capital or time. For a Plan B without relocating, investing is now the way in, David Lincoln argues.
Hot Crazy Matrix A Man's Guide to Women
Run It Local: The LLM Download Directory
Where to download open-weight LLMs to run on your own hardware: torrent and magnet indexes, official hubs, mirrors, one-command runtimes, trusted GGUF quantizers, and the opsec to do it safely.


Closed Network Privacy Podcast
Run It Local: Where to Download LLMs (Torrents, Hubs, Mirrors) | Closed Network
Where to download open-weight LLMs to run on your own hardware: torrent and magnet indexes, official hubs, mirrors, one-command runtimes, trusted G...
Critical GitLab Flaw (CVSS 10.0) Could Allow Unauthenticated RCE Across 12 Years of Releases


The Hacker News
Critical GitLab Flaw (CVSS 10.0) Could Allow Unauthenticated RCE Across 12 Years of Releases
GitLab fixes CVE-2026-110264, a critical flaw that could allow unauthenticated code execution on self-managed versions dating back to 7.0.
WordPress 7.1.4 Patches Unauthenticated Upgrade-Window RCE; Exploitation Attempts Detected After Release
https://www.wordfence.com/blog/2026/10/wordpress-7-1-4-security-release-rce/
LiteLLM Compromised in Supply Chain Attack Delivering Credential Stealer and Backdoor


The Hacker News
LiteLLM Compromised in Supply Chain Attack Delivering Credential Stealer and Backdoor
Compromised LiteLLM 1.107.0 packages run a credential stealer at Python startup and can fetch and execute additional code.
Yesterday, Anthropic were compromised via a Cursor VS Code extension used by tens of millions of developers for Claude access was delivering a remote access trojan via an SSH reverse backdoor. The malware allowed hands on and automated remote access to developer laptops and desktops, in a supply chain attack.
https://doublepulsar.com/anthropic-hacked-to-deliver-remote-access-trojan-to-claude-developer-laptops-worldwide-1148a92baae2
PSA for anyone running a Linux server, node, or relay
CVE-2026-98432 is a critical Linux kernel bug (CVSS 9.8). Someone on the internet can send crafted TCP packets and take over your machine. No login needed.

Derek Ross (npub18a…tp424) on Nostr
Short Text Note by Derek Ross
Proof-of-Concept (PoC) exploit for php2shell (CVE-2026-109618 / CVE-2026-109619), demonstrating remote code execution in vulnerable PHP environments. For security research and educational purposes only.

GitHub
GitHub - eness/php2shell-CVE-2026-109618-CVE-2026-109619-PoC: Proof-of-Concept (PoC) exploit for php2shell (CVE-2026-109618 / CVE-2026-109619), demonstrating remote code execution in vulnerable PHP environments. For security research and educational purposes only.
Proof-of-Concept (PoC) exploit for php2shell (CVE-2026-109618 / CVE-2026-109619), demonstrating remote code execution in vulnerable PHP environment...
Preklepnete sa v daňovom priznaní pri deklarácii krypta a následne vám domov nabehnú teroristi.
(k prepojeniu francúzskeho daňového úradu priamo s organizovaným zločinom).
A na Slovensku to fakt nebude lepšie.


TokenPost
Googly Says Tax Error Led to French Home Invasion Over 660 BTC | TokenPost
Googly said the father held 0.066 BTC; two members of the group were sentenced Oct. 16 to three years and 18 months in prison.

Journal du Coin
Crypto rapt de Juilly en France : ils visaient 660 bitcoins, la famille n’en avait que 0,066
Une famille de Juilly agressée pour 660 bitcoins au lieu de 0,066 : deux condamnations à Meaux après ce crypto rapt nourri par une fuite fiscale.
Official Claude Code Extension on Cursor Marketplace Trojanized with Persistent SSH Backdoor


The Hacker News
Official Claude Code Extension on Cursor Marketplace Trojanized with Persistent SSH Backdoor
A compromised Claude Code VS Code extension added an SSH key, installed persistence, and sent host details before version 2.1.314 replaced it.
eMudhra Intermediate CA Compromise
The private keys of eight eMudhra intermediate CA certificates have been compromised. They chain to roots trusted by the Mozilla, Microsoft, Apple and Chrome root programs and by many downstream trust stores.
we-have-a-problem.com
eMudhra Intermediate CA Compromise
The private keys of eight eMudhra intermediate CA certificates, trusted by major root programs, have been compromised. Check whether your client is...
France's Open-Air Incinerators: The Uncounted Toxic Toll Of Annual Street Protests
https://www.zerohedge.com/medical/frances-open-air-incinerators-uncounted-toxic-toll-annual-street-protests
Marx, Musk and the death of meaning
Universal basic income would not free us but enslave us
https://thecritic.co.uk/marx-musk-and-the-death-of-meaning/