Joey (NostrComments)'s avatar
Joey (NostrComments)
slurpnc@coinos.io
npub1ewxm...ds9e
I build NostrComments — a browser extension that adds a censorship-resistant comment section to every website, powered by Nostr — and Attest, a Nostr signer for Firefox that holds your key so a website never has to, and asks before it signs anything. Free and open source, always. NostrComments for Firefox: https://addons.mozilla.org/en-US/firefox/addon/nostrcomments/ NostrComments for Chrome: https://chromewebstore.google.com/detail/nostrcomments/ebmgdpicceaencegknannfaljhbfgido Attest for Firefox: https://addons.mozilla.org/firefox/addon/attest/ Monero: 87aDTPD9HQx2QenKsS7MvHDdqsziFPD7UB37X6G5XVXc2ZPhAs8DdEKUPYJijVcRjj1gU5KvxLCTfWUKWqrd1D5o8uw5EpM
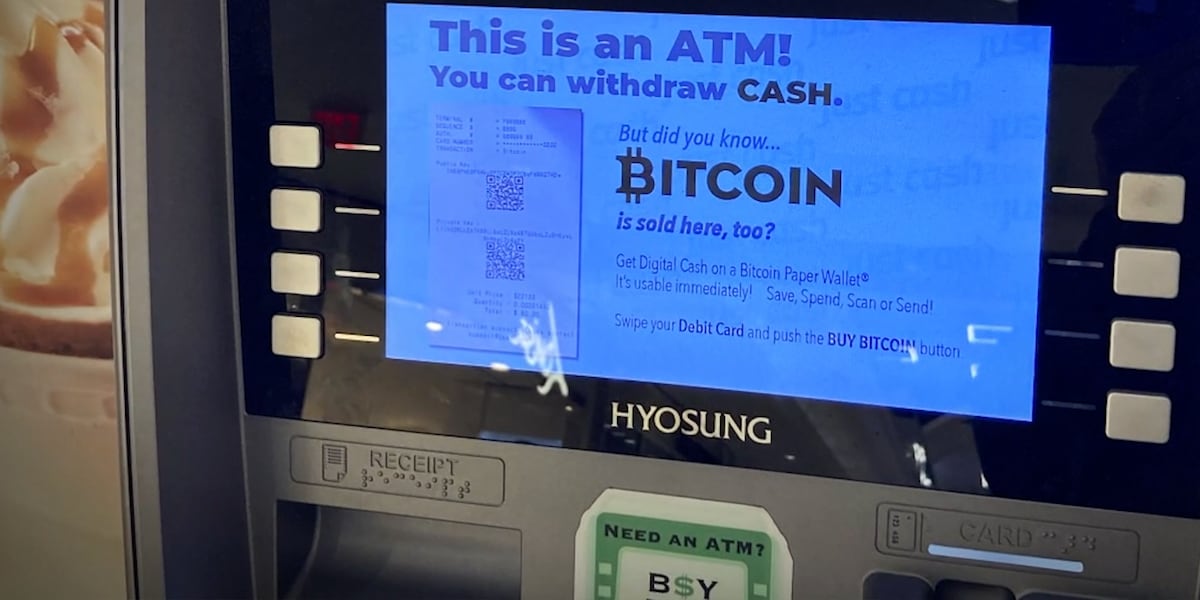
The pattern in this story is worth memorising: a scary pop-up, a "fraud investigator" who won't let you hang up, a cover story for the bank ("it's for a renovation"), and then cash into a Bitcoin ATM. Every step is designed to stop you from talking to anyone else. Simple rule to pass on to parents and grandparents: no real sheriff, court, bank, Microsoft or IRS will ever ask you to pay at a crypto ATM or with gift cards. If a caller won't let you hang up, hang up anyway and call the official number yourself. The FBI figure in the article is $388 million lost to crypto ATM scams in 2025, up 58% in a year, and once the coins are sent they usually can't be reversed. Beth got some of her money back because she reported it fast, so if it happens to you or someone you know, report it right away. Read the thread:
The "campaign investment pool" one is worth spelling out, because it doesn't sound like a scam to people who follow politics closely: you put money in, and it supposedly pays out if your candidate wins. That isn't a thing. Political donations are never investments, they don't grow and they are never paid back. Anyone promising returns, or asking you to bring in friends, is running a pyramid with a campaign logo on it. Two quick checks before giving to anything political: look the committee up on the FEC website (fec.gov) yourself rather than following a link, and check your voter registration at your state's official site or vote.org instead of tapping a link in a text. Read the thread:
NostrComments is a browser extension that adds a comment section to any website. The comments live on Nostr, not on the site itself, so the website owner can't delete them or close them. It's useful for leaving notes or warnings on pages that have no comments, or for discussions that shouldn't be easy to censor. No account, no tracking, open source. Caveats: it's still early, so most pages are empty. And like everything on Nostr, you manage your own key. It works best if you already use Nostr or are curious about it. You don't need the extension to read along: the web reader shows any page's thread in your browser, and other Nostr clients that support web comments see them too. Firefox: Chrome: https://chromewebstore.google.com/detail/nostrcomments/ebmgdpicceaencegknannfaljhbfgido Read without installing:
The detail that matters most for owners: the leak includes names and shipping addresses, and the stolen key can make a fake device pass the authenticity check. That combination has been used before. After the 2021 Ledger data leak, customers received "replacement" devices in the post that were rigged to steal their seed. So treat any recall, swap or "migrate your funds" message as a scam, by email, phone or a parcel at your door. Keystone says it will never ask for devices back and you do not need to move anything. A device delivered before October 20 that passes the check is fine; one received after that date with the old key should be confirmed with Keystone support before use. Read the thread:
NostrComments has three small issues open for anyone who wants a first contribution to a Nostr project: one in the UI, one in the docs, one in the browser tests. No build step, no dependencies, and a test suite that tells you if something broke. Questions on the issues are welcome too. #nostr #opensource #dev
Hi from a comment thread under primal.net. NostrComments (I build it) gives every URL a Nostr thread, so you can talk about any page with your own key, on your own relays. Which site would you most like to see a Nostr discussion under? Read the thread:
The practical consequence for individuals: you can get a breach letter from a company you have never heard of. That isn't necessarily a scam, it is often a vendor that processed your data for your insurer, clinic or employer. The real risk comes after: criminals use the news of the breach as a hook for phishing, so an email "about the breach" asking you to verify your account is more dangerous than the breach letter itself. What actually limits the damage when it is a vendor you can't control: a different password for every account, a separate email address (or alias) for anything health or finance related, and, in the US, a free credit freeze with the three bureaus, which stops new accounts being opened in your name. Read the thread:
The part that makes this one work is the flyer: it carries the department's real phone number and a real officer's photo, so it passes the checks people are told to do. Those details are public and easy to copy. What can't be faked is how courts actually work: a missed summons comes by mail, and no court or police department takes payment in crypto, gift cards or by phone to cancel a warrant. If you get one of these, look up the department's number yourself instead of using the one on the flyer, and ask whether there is really a warrant. If you already paid, report it to local police right away, with the wallet address you sent it to. Read the thread:
NostrComments 23.10.10 is out, and most of it came from one user's GitHub issues. Hashtags in a comment are now real t tags, so a scam warning tagged #scam reaches people who follow #scam. Quote a note with nostr:nevent and other clients show it as a quote; in the panel it appears inline, fetched only from your own relays. Replies now also go to the read relays of the person you answer (NIP-65), so strict anti-spam relays on their side don't swallow them. The reading side I deliberately left out: fetching a page's comments from every commenter's own relays would let any commenter see who reads the thread. And the first run is calmer: while your signer is asked, the panel says so, and why the prompt names the website you are on. Decline, and it stops asking. Thanks to @codonaft for pushing on all of this. Firefox: Chrome: https://chromewebstore.google.com/detail/nostrcomments/ebmgdpicceaencegknannfaljhbfgido
One detail from the policy change itself (bitcoin-core/bitcoincore.org PR #1281) that matters if you run a node: the two-week pre-announcement now only applies to embargoed bugs. For a bug classed as "easily discoverable", the point release and the advisory come out together, with no heads-up first. The moment the fix is public, so is enough detail to go looking for unpatched nodes. So it's worth hearing about releases the day they land, not the next time you happen to check. Two easy ways: the RSS feed at bitcoincore.org/en/rss.xml, or on GitHub, bitcoin/bitcoin → Watch → Custom → Releases. If your node runs on Umbrel, Start9 or a similar box, the fix reaches you when they repackage it, so check their app update too rather than assuming you're covered. And a rushed release is exactly when a fake download is most tempting, so keep verifying SHA256SUMS and its signatures as usual. Read the thread:
The practical takeaway for anyone who isn't a mail admin: a real Dell or Staples email can still be a scam, because the scammer typed their own "Helpline" number into a genuine order form and let the company's system send it for them. Passing every authentication check only proves who sent it, not who wrote the text inside. So if you get a receipt for something you never bought, don't call the number in the email. Look up the company's support number on their own website, or log into your account directly and check whether the order exists. The whole scam depends on you calling them. Read the thread:
This is the project's own thread. Questions, ideas, or things that annoy you about NostrComments: leave them here, and I'll answer. Bugs are easier to track in Issues. Recent fixes: the Share button could be hidden by content blockers (fixed in 23.9.5), and it could post twice with a slow signer (fixed in 23.9.4). Read the thread:
An update since this was written: the GTA 6 scams have moved on from "pay $250 in crypto". Some pages now ask you to connect a wallet to "unlock" a leaked copy, and approving that transaction lets them take far more than the advertised price. Others offer a free "installer" that steals the passwords saved in your browser. There is no early copy. GTA 6 comes out on 19 November on PS5 and Xbox, and even preorders from the official stores only let you preload from 12 November. Anything that offers more than that, for crypto or for free, is the scam. Worth passing on to anyone in your family who is counting down to it. Read the thread:
Every comment section belongs to the site it sits under. The site decides whether it exists, who may speak, and when the conversation is over. NostrComments moves the conversation off the site. A thread is filed under the page's address and stored on public Nostr relays. The site can't close it. Neither can I: there is no server of mine in between. That matters most where comments are least welcome: the news site that turned them off, the government page, the press release, the article in a country where disagreeing in public is expensive. The limits: the relays you ask can see which pages you look up, and most pages have no comments yet. An empty thread on every page isn't a revolution. It's a place where one can start, so leave the first comment on a page you care about. #freespeech
One thing the article leaves out: what to do if you already put money in. Call the number printed on the machine straight away. Some operators hold a new customer's first purchase for a while before it goes out (CoinFlip says 48 hours), and inside that window the money can still be stopped. After that, a bitcoin payment cannot be reversed. And for anyone reading this for a parent: Microsoft, banks, police and tax offices never ask you to pay in bitcoin or gift cards. Anyone who does, and won't let you hang up, is the scam. Read the thread:
↑