CyberSatoshi ๐“†™'s avatar
CyberSatoshi ๐“†™
XBToshi@kyc.rip
npub10hqc...4fln
Bitcoin & Monero Maxi. 1 $XMR > 1 $BTC. (priv/acc)๐Ÿˆโ€โฌ› dev of https://kyc.rip | https://xmr.club | https://xmr402.org | https://walls.rip | https://stables.rip | https://ripley.run ๐Ÿ”€ Get $XMR โ†’ https://kyc.rip/swap โฌ‡๏ธ Wallet: https://ripley.run/terminal
CyberSatoshi ๐“†™'s avatar
XBToshi 22 hours ago
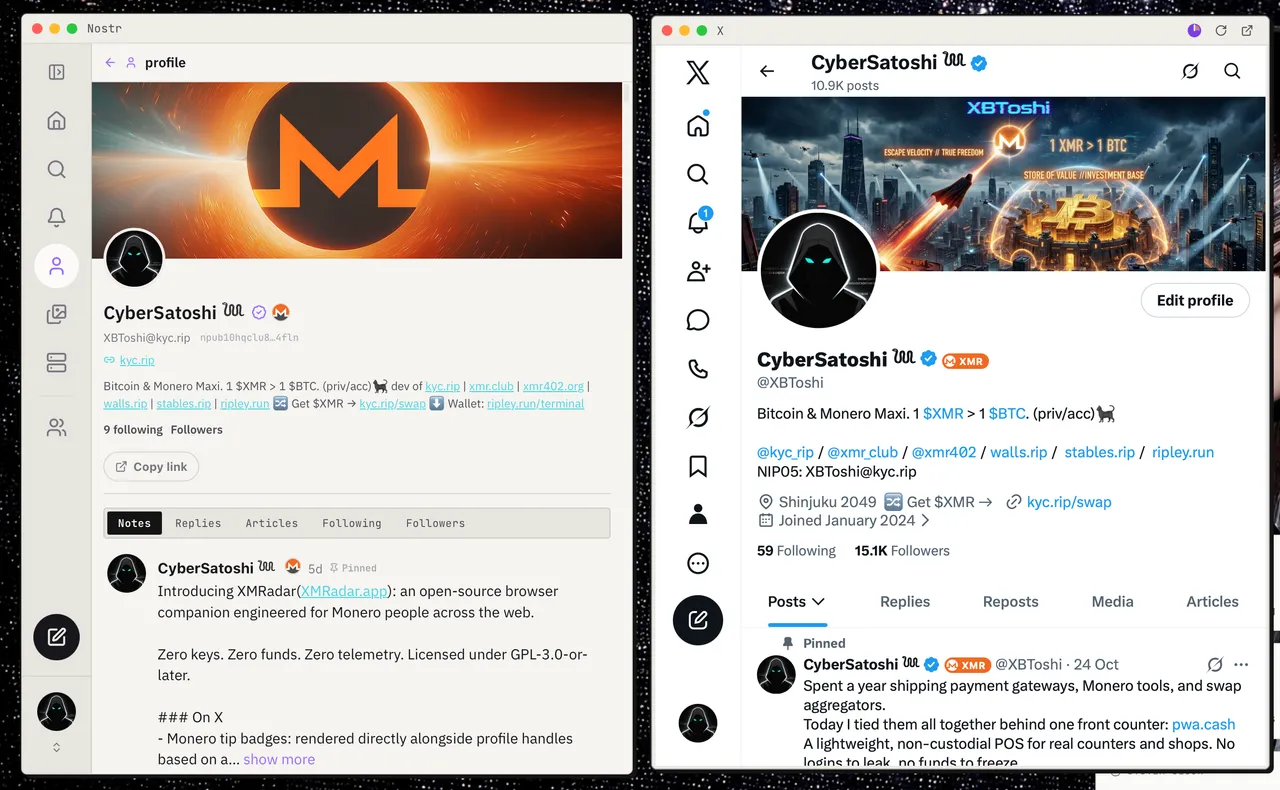
image Rate my desktop. #nostr #desktop
CyberSatoshi ๐“†™'s avatar
XBToshi yesterday
A swap sends you a "letter of guarantee" before you pay. A PGP signature is only worth something if you verify it against the key you already pinned. Save the letter, check the fingerprint, then send. A screenshot of a signature proves nothing. If you'd rather not do it by hand: XMRadar, our browser extension, saves the letter and checks the signature and NKIP-0001 receipts against the addresses on the page. Check more details: https://xmr.club/tools/xmradar. #pgp #xmr #xmradar #nki
CyberSatoshi ๐“†™'s avatar
XBToshi yesterday
Critical Security Alert for Web3 & Crypto Traders: A fresh zero-day RCE bypasses Telegram Desktop 7.4.3 on Windows even that version is "patched". A simple bot interaction card can execute arbitrary code on your machine with no external download prompts. Why patches are failing: Telegramโ€™s new in-message widgets run on QuickJS inside the main process without process isolation. Actionable steps: โ€ข Never trigger interactive bot cards from unknown accounts. โ€ข Keep signing keys strictly off machines running Windows Telegram Desktop. โ€ข Use mobile clients (isolated by OS sandboxes) for sensitive communications. #telegram #windows #rce #quickjs #web3 image
CyberSatoshi ๐“†™'s avatar
XBToshi yesterday
The FBI just warned that North Korea stole $400M+ via "FaceStealer" fake job/advisory lures. Want to see what their actual bait looks like? Here is what lands in Web3 devs' inboxes every week: Look at the identical copy-paste scripts across fake teams: โ€ข "Velixus Labs" vs "J-Soft Labs" โ€ข EXACT same buzzword soup: "gaming, DEXs, and crypto real estate" โ€ข Ridiculous pay: $150-$200/hr for remote "Technical Leader / Advisor" โ€ข Pushing you onto Telegram or Calendly If you join that call: 1. They play stolen webcam footage of a previous victim to build trust. 2. Claim an "audio glitch" and ask you to run a quick terminal "fix" script. 3. Your local keys, browser wallets, and Telegram sessions are completely drained. 4. Or assign you a task to clone their repo where dangerous code runs when you do 'npm install' or 'pip install'. If an email pitches "gaming + DEX + crypto real estate", hit block immediately. Itโ€™s Lazarus. ๐Ÿฅท #northkorea #facestealer #lazarus #web3 #phishing
CyberSatoshi ๐“†™'s avatar
XBToshi yesterday
Microsoft: "We rolled out cryptographic HMAC log signing to permanently kill CLFS exploits." MSNightmare: "Awesome, we just tricked Microsoft Defender into signing our arbitrary symlinks for free SYSTEM shells." Meet "SignDrop": an unpatched Windows 0-day that uses the security feature as the attack vector. Peak Windows security poetry. ๐Ÿ˜‚ The exploit achieves instant NT AUTHORITY\SYSTEM by weaponizing the exact mitigation Microsoft shipped to stop CLFS exploits. The Chain: 1. Microsoft deployed HMAC log integrity (.cnpf files) to block tampered clfs.sys logs. 2. An attacker crafts a CLFS log and creates an Object Manager symlink. 3. Coerces Microsoft Defender (MsMpEng.exe) into scanning the target. 4. clfs.sys auto-generates the missing .cnpf file as SYSTEM, but inherits the attacker's DACL. 5. Arbitrary write primitive = immediate privilege escalation. Affects Windows 11 (25H2/26H2) & Server 2025. No CVE, no patch. PoC is public. #hmac #clfs #windows #msft #exploit image
CyberSatoshi ๐“†™'s avatar
XBToshi yesterday
Microsoft: "We rolled out cryptographic HMAC log signing to permanently kill CLFS exploits." MSNightmare: "Awesome, we just tricked Microsoft Defender into signing our arbitrary symlinks for free SYSTEM shells." Meet "SignDrop": an unpatched Windows 0-day that uses the security feature as the attack vector. Peak Windows security poetry. ๐Ÿ˜‚ The exploit achieves instant NT AUTHORITY\SYSTEM by weaponizing the exact mitigation Microsoft shipped to stop CLFS exploits. The Chain: 1. Microsoft deployed HMAC log integrity (.cnpf files) to block tampered clfs.sys logs. 2. An attacker crafts a CLFS log and creates an Object Manager symlink. 3. Coerces Microsoft Defender (MsMpEng.exe) into scanning the target. 4. clfs.sys auto-generates the missing .cnpf file as SYSTEM, but inherits the attacker's DACL. 5. Arbitrary write primitive = immediate privilege escalation. Affects Windows 11 (25H2/26H2) & Server 2025. No CVE, no patch. PoC is public. image
CyberSatoshi ๐“†™'s avatar
XBToshi 4 days ago
Complaining that the Motorola Signature 27 costs โ‚ฌ1,899 misses how low-level silicon security works. People treat phone tiers like a slider: pay less, get a dimmer screen or plastic back. In exploit mitigation, that slider does not exist. Hardware memory tagging (MTE) is not a luxury finish. It is an ARMv9 primitive. Chipmakers strip MTE and secure element isolation from mid-range dies to save area and margin. If an SoC cannot enforce hardware memory safety, GrapheneOS loses its core defense against zero-day memory corruption. Shipping on stripped silicon to hit โ‚ฌ499 turns the OS into privacy theater. Breaking the Pixel hardware monopoly required an OEM willing to unlock bootloader attestation on cutting-edge silicon. That overhead hits flagship tiers first. โ‚ฌ1,899 hurts, but building a cheap phone by discarding memory safety primitives is not an alternative. It is snake oil. #monero #privacy #siliconsecurity #mte #grapheneos
CyberSatoshi ๐“†™'s avatar
XBToshi 5 days ago
From PoC disclosure to a fully weaponized GUI utility in hours. Filza-WQ drops for iOS 27.0โ€“27.3 beta: - Zero jailbreak required. - Wraps the container-query sandbox escape from @forcequitOS and @0xjohnny. - Instant read/write access to ConfigurationProfiles, MobileGestalt cache, and System Data containers from an unsigned IPA. Apple spends billions selling the illusion of containerized security. A sideloaded file browser just bypassed the entire walled-garden sandbox to browse system-level app state like a desktop directory. When the boundary between an isolated app sandbox and system storage reduces to a single repackaged binary, the mobile threat model is broken. image Repo: #monero #apple #ios #gui #filza image
CyberSatoshi ๐“†™'s avatar
XBToshi 5 days ago
[ SYSTEM_STATUS_UPDATE ] xmrprice.live ------------------------ ๐Ÿ’ต CEX Price : $607.81 ๐Ÿด Street Price: $615.12 โšก Premium : +1.20% ๐Ÿ“Š 24H: 23,265 TXs ๐Ÿ›ก๏ธ OBS_Node : 73.8% ๐Ÿ’ง P2P_LIQ : 7,358.07 XMR ------------------------ SOURCE: AGG (TR+CN+NK+HV) ๐ŸŒ Anonymous eSIM: Mobile data plans from 100+ countries. No ID, no trace. Pay with XMR, Lightning, or USDT. #XMR #MONERO #PRIVACY #NoKYC
CyberSatoshi ๐“†™'s avatar
XBToshi 6 days ago
- June 2026: US Treasury tweets about sanctioning an Iranian exchange. ZachXBT replied under their post with a flow chart: "You should sanction these shady Canadian OTC brokers, they're washing crypto from violent home invasions." - November 2026: US Treasury officially sanctioned eight Canadian OTCs, explicitly hitting the exact two brokers ZachXBT pointed out. A trillion-dollar compliance apparatus with thousands of intelligence officers and ChainAlysis subscriptions, literally taking targeting cues from replies under their X posts. Unregulated Canadian MSB storefronts remain the biggest laundry in North America, and it takes an anonymous anime PFP to do FINTRAC's job for them. #monero #sanctions #canada #crypto #otc image
CyberSatoshi ๐“†™'s avatar
XBToshi 6 days ago
Web3Auth raised tens of millions preaching โ€œnon-custodial MPCโ€ and โ€œusers own their keys.โ€ Todayโ€™s reality: a vulnerability hits their backend, and Web3Auth runs a script that sweeps $3M across 19 chains without a single signature confirmation from any user device. Read that again, slowly. If a company can drain your balance while youโ€™re asleep and tweet โ€œrelax guys, that was our whitehat sweeper bot front-running the hacker,โ€ you never had a self-custodial wallet. You had a centralized database with a Web3 splash screen and an OAuth middleman. The entire โ€œseedless onboardingโ€ narrative was just a VC cartel selling Web2 convenience at the cost of giving a random node cluster full spend authority over your stack. You didnโ€™t kill the middleman. You just gave him root access. #monero #selfcustody #whitehat #vc #node image
CyberSatoshi ๐“†™'s avatar
XBToshi 6 days ago
Checked how much have they managed to secure ahead of the hacker, it turns out it's much more wild than we suspected earlier: - Total 19 chains are affected, secured funds almost $3 millions at current market price. - Mainly Cosmos, Injective, Akash, Osmosis, Celestia and Nobel. - dYdX and all EVM chains, Axelar, Babylon, Saga and Agoric counted 200K total. This is still ongoing. #monero #cosmos #dydx #evm #akash
CyberSatoshi ๐“†™'s avatar
XBToshi 6 days ago
Anthropic: "Claude Code gives developers superpowers." Apiiro research: 1,122 public GitHub repos just leaked 2,539 plaintext production credentials. How it works: 1. Developer runs a psql/ssh command with a plaintext password. 2. Clicks "yes, and don't ask again". 3. Claude Code saves the literal commandโ€”secrets includedโ€”into .claude/settings.local.json. 4. Instead of writing to the project .gitignore, it writes to local global Git excludes. 5. Developer or Claude's auto-commit pushes to main. 379 database passwords, 43 root SSH keys, 122 Supabase tokens on public GitHub. The bug was reported months ago and closed by a stale-bot as "not planned." Top modern DevSecOps. image # 1. Check if there is such a configuration item and the sensitive commands. cat .claude/settings.local.json 2>/dev/null | grep -iE 'password|token|key|secret' # 2. Check Git commit history git log --all --full-history -- "**/settings.local.json" # 3. If so, you'd have to rotate your keys first, then clear up your git history. Original news: https://thehackernews.com/2026/11/claude-codes-dont-ask-again-file.html. #devsecops #github #psql #ssh #supabase
CyberSatoshi ๐“†™'s avatar
XBToshi 6 days ago
[ SYSTEM_STATUS_UPDATE ] xmrprice.live ------------------------ ๐Ÿ’ต CEX Price : $598.18 ๐Ÿด Street Price: $605.45 โšก Premium : +1.21% ๐Ÿ“Š 24H: 23,088 TXs ๐Ÿ›ก๏ธ OBS_Node : 72.6% ๐Ÿ’ง P2P_LIQ : 11,128.04 XMR ------------------------ SOURCE: AGG (TR+CN+NK+HV) ๐Ÿ’ธ Dispenser Protocol: Batch privacy payments. Send XMR, BTC, or ETH to multiple recipients in a single transaction. #XMR #MONERO #PRIVACY #NoKYC
CyberSatoshi ๐“†™'s avatar
XBToshi 6 days ago
A warning sign worth knowing: a swap suddenly raises its minimum order, say from $100 to $1,000, while cutting its fee. Sometimes it's a fix for a liquidity problem. Sometimes payouts stall soon after. Either way: keep orders small and save your deposit TXID. #Monero
โ†‘